Guide
NIS2 supply chain: what happens between two questionnaires
Supply chain security under NIS2: what Austria's NISG 2026 and Germany's BSIG require, where questionnaires end and how to monitor suppliers continuously.
- 6 min read
blacklens.io finds exposed systems, exploitable vulnerabilities and leaked credentials and tells you what to fix first.
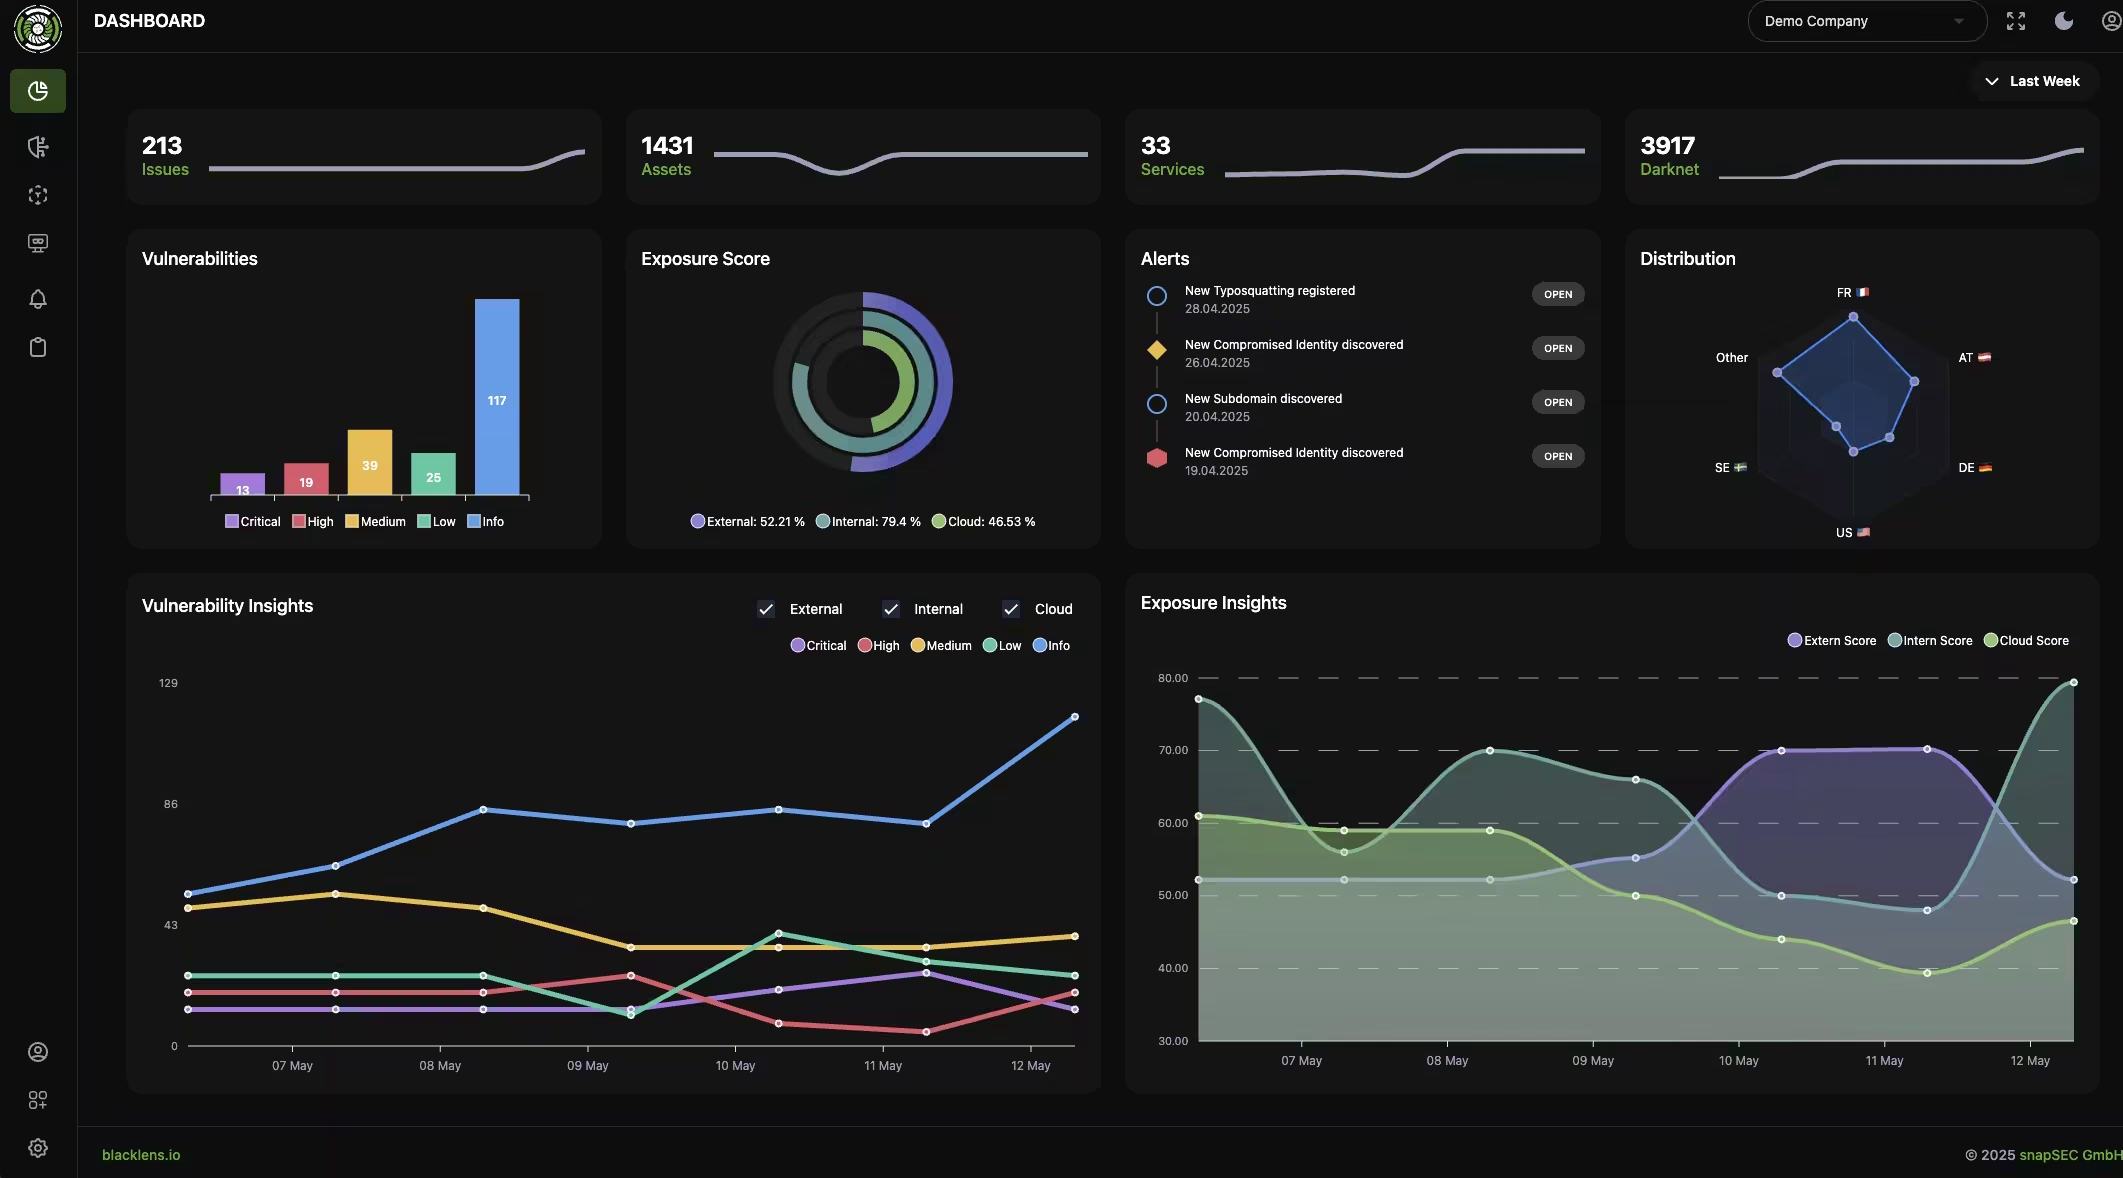
Visuals show sample data.
Used by manufacturers, retailers, software companies and IT service providers across the DACH region.


How it works
Four steps, one platform: find what is exposed, assess what matters, get early warnings and prove the fix.
Step 1 of 4
Visuals show sample data.
blacklens.io finds external, internal and cloud assets automatically, including forgotten systems, shadow IT and lookalike domains.
Explore Attack Surface Management
| AWS | Microsoft 365 | Microsoft Azure | Google Cloud | |
|---|---|---|---|---|
| Resource publicly accessible | High | Not applicable | Passed | Passed |
| Admin accounts without MFA | Passed | Critical | Passed | Passed |
| VM with public IP | Passed | Not applicable | Medium | Passed |
| Public API endpoint | Passed | Not applicable | Passed | Medium |
EPSS, CISA KEV and exploit status show what really matters. AI explains every finding, running as a self-hosted LLM in Europe.
Explore Vulnerability Management
New CVEs are matched against your inventory in real time. We also flag leaked identities and suppliers that appear on leak sites or slip in their weekly rating.
New victims on ransomware leak sites, last 24 hours
One workflow for every finding: assign, fix, close automatically after the re-scan and prove progress with reports.
Explore Unified Vulnerability Management
Visuals show sample data.
blacklens.io shows the whole picture: external, internal, cloud, dark web and suppliers, in one platform and prioritised by real risk.
Finds every domain, service and technology, including the forgotten ones.
200,000+ tests, prioritised by EPSS, CISA KEV and exploit status instead of CVSS alone.
Employees 41Customers 87
469418Leaked accounts with IAM context: privileged, without MFA or password unchanged since the leak.
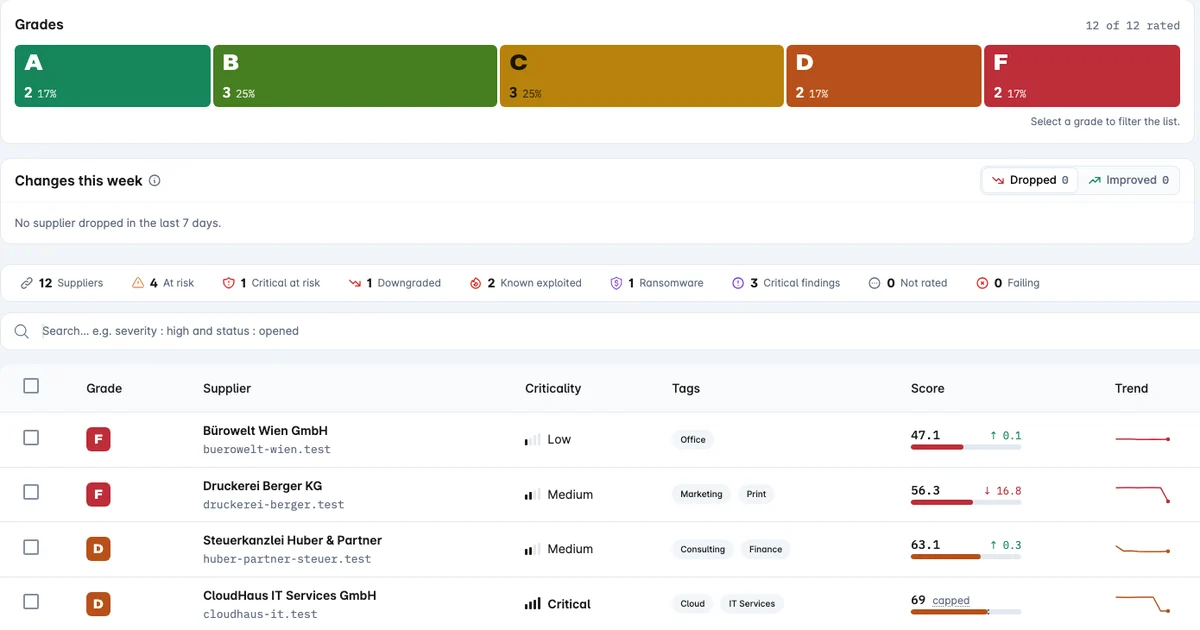
Rates your suppliers from the outside every week with a grade from A to F and alerts you when risk rises.
New CVEs matched in real time against your inventory and verified automatically.
Servers, clients, OT and Active Directory behind the firewall.
Pentesters validate findings manually, with retest and report inside the platform.
Alerts in Jira, Teams, Slack, Sentinel or Elastic. Everything via REST API too.
Visuals show sample data.
Platform
Every source feeds one analysis that prioritises by real risk. The result: tasks, reports and alerts in the tools you already use.
What attackers can see: from outside, in the internal network, in the cloud, on the dark web and at your suppliers.
Prioritised by exploitability, explained in plain language and verified.
Assigned, documented and where your team already works.
Dark Web Monitoring
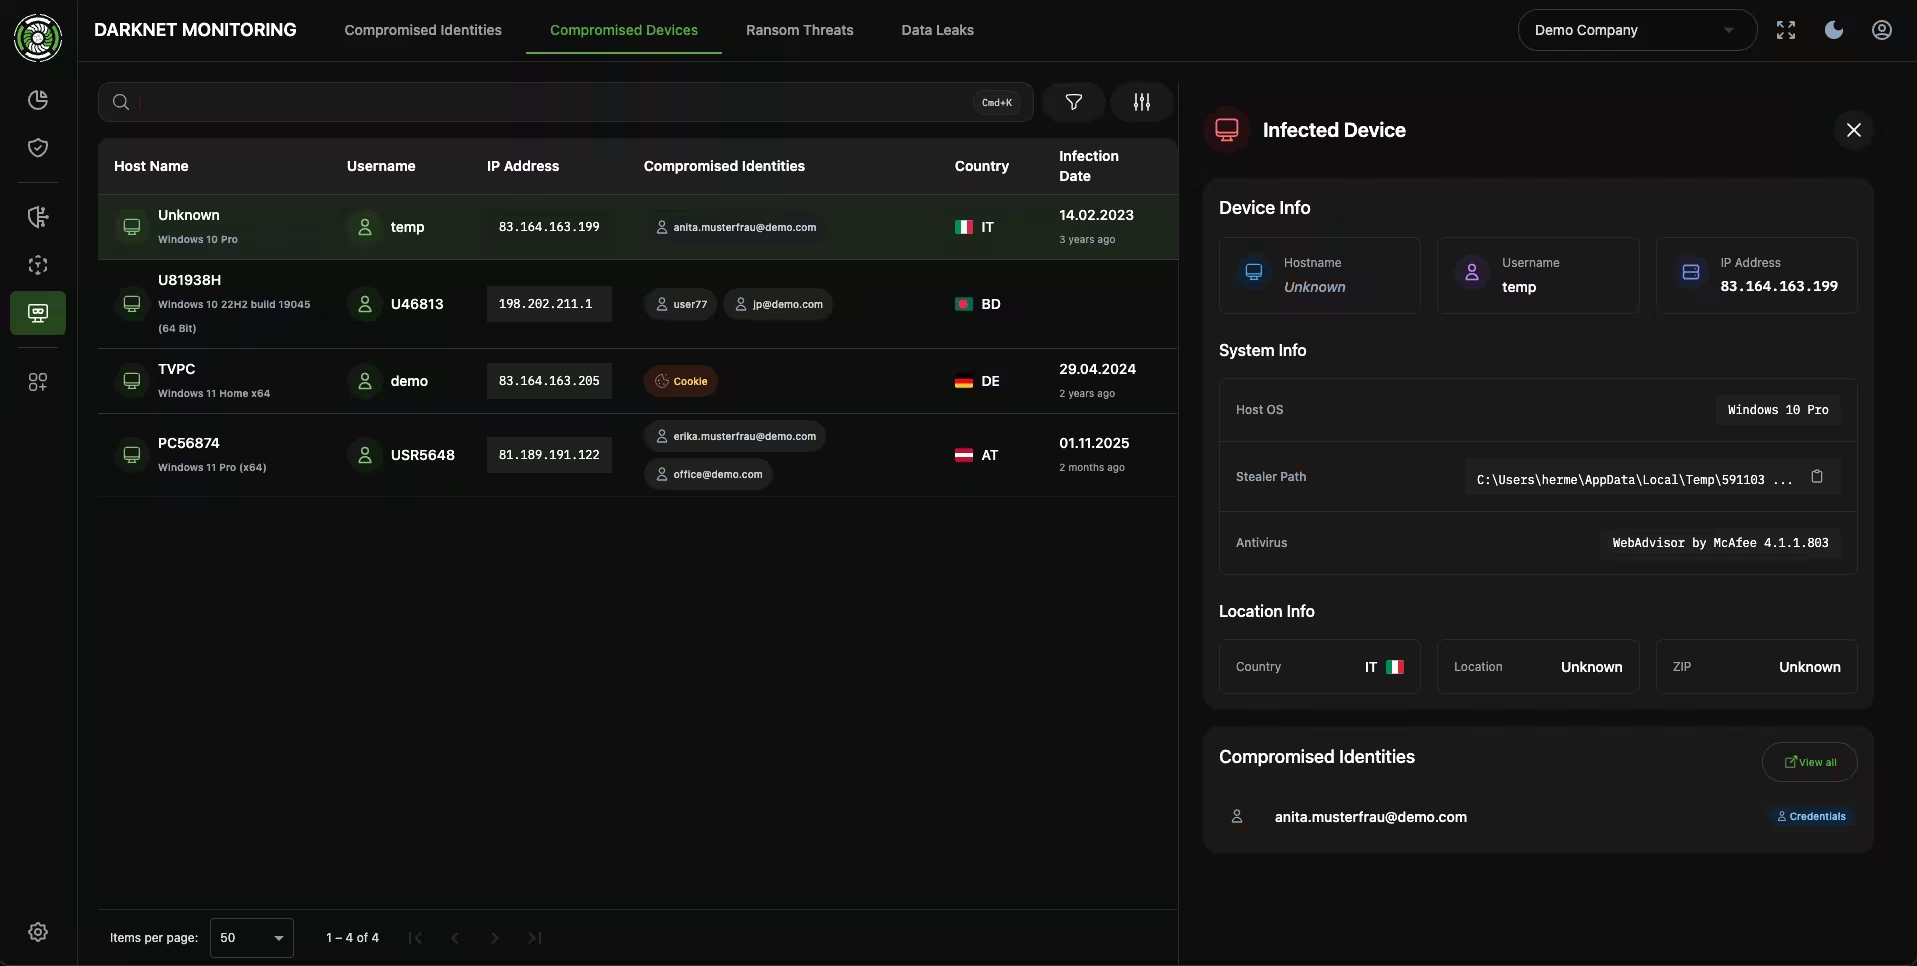
Access brokers sell entry points before ransomware groups strike. blacklens.io finds compromised accounts, infected devices and stolen session cookies and turns them into findings.
m.hu•••@beispiel-gmbh.at
Stealer log, 2 h ago
IAMPrivilegedNo MFA
Visuals show sample data.
Data sovereignty
Platform, scanners and AI run on European infrastructure, built and operated by an Austrian company.
ISO 27001 and SOC 2 certified data centres, our own scanners only in Austria, Germany and Switzerland.
No external AI providers, consent per workspace.
snapSEC GmbH in Vorchdorf, German-speaking support.
Priced by assets, users and suppliers, reports, API and integrations included.
Experiences from manufacturing, retail, software and IT services.
“blacklens.io is the ideal complement to our internal IT security measures. It continuously checks our externally reachable systems, tells us when action is needed and is an important building block of our cyber defence.”
“We were looking for a tool for automated penetration tests. What we found was a platform that lets us identify far more than potential entry points. Real added value for our SecOps.”
“blacklens.io helps us meet the state of the art by flagging vulnerabilities on externally available services very quickly. Together with dark web monitoring, visibility of IT and information security risks improved significantly.”
“blacklens.io helps us maintain an effective cyber defence internationally, permanently instead of one-time shots. It also keeps telling us whether ransomware threats endanger our supply chain.”
“With blacklens.io we have an excellent tool for proactive monitoring of all services and firewall configurations. It saves time and resources, and the reports immediately show where public services can be improved.”
“The blacklens.io package delivers relevant security information about your IT environment. It helps meet legal NIS requirements and, overall, makes an administrator's life more carefree.”
Supply chain security under NIS2: what Austria's NISG 2026 and Germany's BSIG require, where questionnaires end and how to monitor suppliers continuously.
HTTP2Shell is not a new flaw but CVE-2026-111497 in any software with a Brotli decoder. Who is affected, and why the version number misleads.
Node2Shell exploits a flaw in the Brotli decoder that Node.js bundles. The fix ships in Node 22.23.4, 24.22.1 and 26.12.1 – and in Brotli itself.
Get started
We set up your workspace and walk you through the first findings.
Three steps to your first priority
Visuals show sample data.