
Supply chain shock: CrowdStrike npm packages compromised
Compromised CrowdStrike npm packages ship a malicious bundle.js that steals secrets and uses GitHub Actions to gain a lasting foothold in repositories.
- by blacklens.io Team
- Published
- Updated
- 4 min read
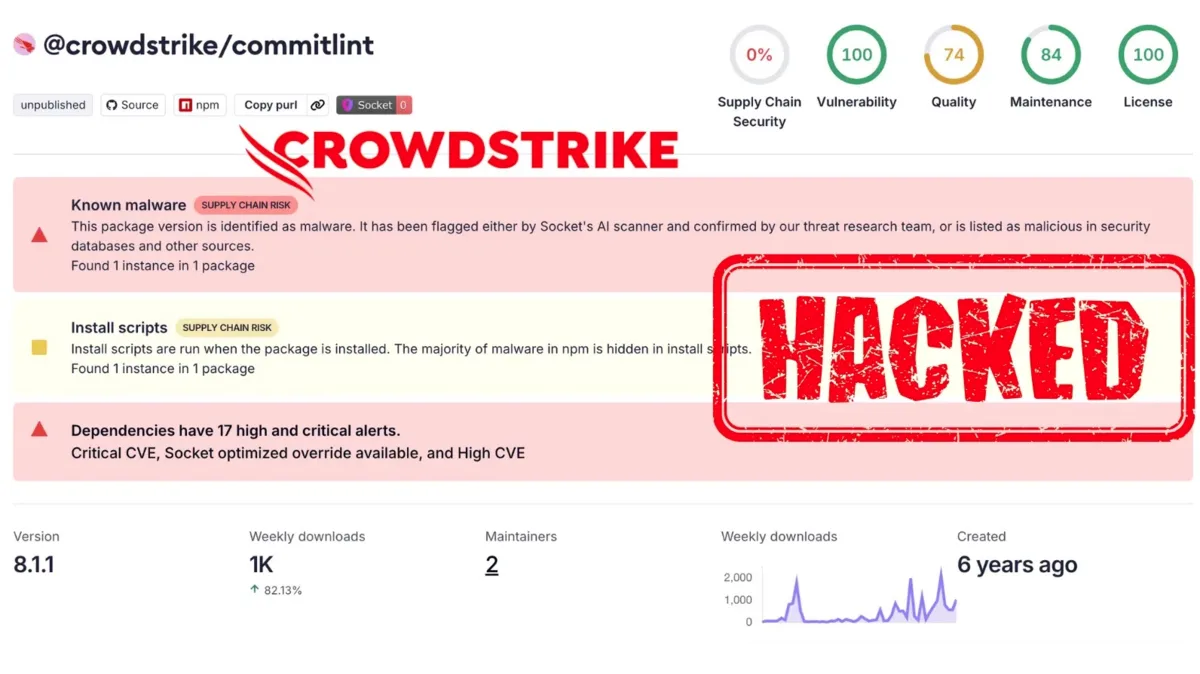
Once again, a large-scale supply chain attack has shaken the open-source community: several npm packages from CrowdStrike have been compromised.
Numerous infected npm packages were published through the crowdstrike-publisher account. Hundreds of other compromised third-party packages are affected as well; the ones known so far are listed at the end of this post. If you use any of these packages, we recommend checking the indicators of compromise (IOCs) immediately and rotating all secrets.
Indicators of compromise
SHA-256 hashes of known variants of the malicious bundle.js:
de0e25a3e6c1e1e5998b306b7141b3dc4c0088da9d7bb47c1c00c91e6e4f85d6
81d2a004a1bca6ef87a1caf7d0e0b355ad1764238e40ff6d1b1cb77ad4f595c3
83a650ce44b2a9854802a7fb4c202877815274c129af49e6c2d1d5d5d55c501e
4b2399646573bb737c4969563303d8ee2e9ddbd1b271f1ca9e35ea78062538db
dc67467a39b70d1cd4c1f7f7a459b35058163592f4a9e8fb4dffcbba98ef210c
46faab8ab153fae6e80e7cca38eab363075bb524edd79e42269217a083628f09
b74caeaa75e077c99f7d44f46daaf9796a3be43ecf24f2a1fd381844669da777
Exfiltration endpoint (defanged):
hxxps://webhook[.]site/bb8ca5f6-4175-45d2-b042-fc9ebb8170b7
What is Shai-Hulud?
Researchers named the campaign "Shai-Hulud" after its YAML workflow file. It continues the attacks that had already hit the widely used @ctrl/tinycolor package. It is a different incident from the phishing attack on chalk, debug and other packages on 8 September 2025.
Affected CrowdStrike packages include @crowdstrike/commitlint, @crowdstrike/foundry-js, @crowdstrike/glide-core and several @crowdstrike/logscale-* packages. The full list is at the end of this post.
How the attack works
The attack runs in five steps:
- Injecting the payload: a manipulated
bundle.jswas added to the compromised packages. - Fetching a secret scanner: as soon as the script runs, it downloads TruffleHog, a legitimate open-source tool that is meant to find accidentally published secrets.
- Collecting and validating secrets: the tool searches the infected instances for API tokens, GitHub access tokens, npm tokens, cloud credentials (e.g. AWS keys) and many other secrets, and validates them.
- Persistence via GitHub Actions: an unauthorised GitHub Actions workflow file (
shai-hulud-workflow.yml) is then written to the target repository. It remains even after the compromised package has been removed. The next time the pipeline runs, the workflow can execute again and exfiltrate data. - Exfiltration: all collected information is sent to a hard-coded webhook controlled by the attacker.
Impact and recommendations
CrowdStrike stresses that the compromised npm packages are not part of the Falcon sensor platform and that customers of the product are not affected. The company quickly removed the packages from the public registry and rotated its keys.
All organisations should nevertheless:
- Check CI/CD pipelines and developer laptops: review installed npm packages for the compromised versions.
- Rotate all npm tokens and other secrets: renew any unauthorised access tokens immediately.
- Monitor logs: suspicious
npm publishevents or unexpected changes to GitHub workflows indicate persistence attempts.
Why proactive protection matters
Some of the affected packages belong to the popular NativeScript framework or to development SDKs from start-ups. The long list and the renewed naming of the YAML workflow as "shai-hulud" show that this campaign reaches far beyond CrowdStrike. Supply chain attacks are becoming more professional, complete with deliberate branding.
The attackers use legitimate security tools such as TruffleHog and hide their operations in common DevOps workflows. Waiting for a registry operator to remove compromised packages is no longer enough.
How blacklens.io helps
Checking package versions in pipelines and on developer machines remains a job for the steps above. blacklens.io covers the attack surface your organisation exposes to the outside:
- Early warning for new vulnerabilities: new CVEs are continuously matched against the technologies on your attack surface and verified with a scan where a verification template exists. Alerts reach the responsible team by e-mail, push notification or integrations such as Jira, Microsoft Teams or Slack.
- Visibility of your attack surface: continuous Attack Surface Management shows which assets, services and technologies are reachable from the outside. When a vulnerability becomes known in a specific product, you can quickly see which of your assets may be affected.
- Faster prioritisation: for every Threat Center match, blacklens.io shows the affected assets and signals such as CVSS, EPSS, KEV listing and available exploits at a glance. This saves time in assessment and containment.
- Trust and compliance: showing that you have your supply chain risks under control strengthens the trust of customers and partners. Many industry standards and regulators now require supply chain risk management, and blacklens.io supports you with the evidence and reports you need.
Conclusion
The continuing attacks on the npm supply chain show how urgently proactive security measures are needed. The compromised CrowdStrike packages are only the tip of the iceberg: the Shai-Hulud campaign has already infected hundreds of other packages and uses DevOps automation to spread.
Review your software supply chain now, rotate secrets regularly and put mechanisms in place that detect suspicious activity early. With blacklens.io, organisations also keep continuous track of their external attack surface and the new vulnerabilities that affect it.
Compromised packages and versions
The following npm packages and versions had been confirmed as affected at the time of publication (grouped by package):
@ahmedhfarag/ngx-perfect-scrollbar: 20.0.20@ahmedhfarag/ngx-virtual-scroller: 4.0.4@art-ws/common: 2.0.28@art-ws/config-eslint: 2.0.4, 2.0.5@art-ws/config-ts: 2.0.7, 2.0.8@art-ws/db-context: 2.0.24@art-ws/di-node: 2.0.13@art-ws/di: 2.0.28, 2.0.32@art-ws/eslint: 1.0.5, 1.0.6@art-ws/fastify-http-server: 2.0.24, 2.0.27@art-ws/http-server: 2.0.21, 2.0.25@art-ws/openapi: 0.1.9, 0.1.12@art-ws/package-base: 1.0.5, 1.0.6@art-ws/prettier: 1.0.5, 1.0.6@art-ws/slf: 2.0.15, 2.0.22@art-ws/ssl-info: 1.0.9, 1.0.10@art-ws/web-app: 1.0.3, 1.0.4@crowdstrike/commitlint: 8.1.1, 8.1.2@crowdstrike/falcon-shoelace: 0.4.1, 0.4.2@crowdstrike/foundry-js: 0.19.1, 0.19.2@crowdstrike/glide-core: 0.34.2, 0.34.3@crowdstrike/logscale-dashboard: 1.205.1, 1.205.2@crowdstrike/logscale-file-editor: 1.205.1, 1.205.2@crowdstrike/logscale-parser-edit: 1.205.1, 1.205.2@crowdstrike/logscale-search: 1.205.1, 1.205.2@crowdstrike/tailwind-toucan-base: 5.0.1, 5.0.2@ctrl/deluge: 7.2.1, 7.2.2@ctrl/golang-template: 1.4.2, 1.4.3@ctrl/magnet-link: 4.0.3, 4.0.4@ctrl/ngx-codemirror: 7.0.1, 7.0.2@ctrl/ngx-csv: 6.0.1, 6.0.2@ctrl/ngx-emoji-mart: 9.2.1, 9.2.2@ctrl/ngx-rightclick: 4.0.1, 4.0.2@ctrl/qbittorrent: 9.7.1, 9.7.2@ctrl/react-adsense: 2.0.1, 2.0.2@ctrl/shared-torrent: 6.3.1, 6.3.2@ctrl/tinycolor: 4.1.1, 4.1.2@ctrl/torrent-file: 4.1.1, 4.1.2@ctrl/transmission: 7.3.1@ctrl/ts-base32: 4.0.1, 4.0.2@hestjs/core: 0.2.1@hestjs/cqrs: 0.1.6@hestjs/demo: 0.1.2@hestjs/eslint-config: 0.1.2@hestjs/logger: 0.1.6@hestjs/scalar: 0.1.7@hestjs/validation: 0.1.6@nativescript-community/arraybuffers: 1.1.6, 1.1.7, 1.1.8@nativescript-community/gesturehandler: 2.0.35@nativescript-community/perms: 3.0.5, 3.0.6, 3.0.7, 3.0.8@nativescript-community/sentry: 4.6.43@nativescript-community/sqlite: 3.5.2, 3.5.3, 3.5.4, 3.5.5@nativescript-community/text: 1.6.9, 1.6.10, 1.6.11, 1.6.12, 1.6.13@nativescript-community/typeorm: 0.2.30, 0.2.31, 0.2.32, 0.2.33@nativescript-community/ui-collectionview: 6.0.6@nativescript-community/ui-document-picker: 1.1.27, 1.1.28@nativescript-community/ui-drawer: 0.1.30@nativescript-community/ui-image: 4.5.6@nativescript-community/ui-label: 1.3.35, 1.3.36, 1.3.37@nativescript-community/ui-material-bottom-navigation: 7.2.72, 7.2.73, 7.2.74, 7.2.75@nativescript-community/ui-material-bottomsheet: 7.2.72@nativescript-community/ui-material-core-tabs: 7.2.72, 7.2.73, 7.2.74, 7.2.75, 7.2.76@nativescript-community/ui-material-core: 7.2.72, 7.2.73, 7.2.74, 7.2.75, 7.2.76@nativescript-community/ui-material-ripple: 7.2.72, 7.2.73, 7.2.74, 7.2.75@nativescript-community/ui-material-tabs: 7.2.72, 7.2.73, 7.2.74, 7.2.75@nativescript-community/ui-pager: 14.1.36, 14.1.37, 14.1.38@nativescript-community/ui-pulltorefresh: 2.5.4, 2.5.5, 2.5.6, 2.5.7@nexe/config-manager: 0.1.1@nexe/eslint-config: 0.1.1@nexe/logger: 0.1.3@nstudio/angular: 20.0.4, 20.0.5, 20.0.6@nstudio/focus: 20.0.4, 20.0.5, 20.0.6@nstudio/nativescript-checkbox: 2.0.6, 2.0.7, 2.0.8, 2.0.9@nstudio/nativescript-loading-indicator: 5.0.1, 5.0.2, 5.0.3, 5.0.4@nstudio/ui-collectionview: 5.1.11, 5.1.12, 5.1.13, 5.1.14@nstudio/web-angular: 20.0.4@nstudio/web: 20.0.4@nstudio/xplat-utils: 20.0.5, 20.0.6, 20.0.7@nstudio/xplat: 20.0.5, 20.0.6, 20.0.7@operato/board: 9.0.36, 9.0.37, 9.0.38, 9.0.39, 9.0.40, 9.0.41, 9.0.42, 9.0.43, 9.0.44, 9.0.45, 9.0.46@operato/data-grist: 9.0.29, 9.0.35, 9.0.36, 9.0.37@operato/graphql: 9.0.22, 9.0.35, 9.0.36, 9.0.37, 9.0.38, 9.0.39, 9.0.40, 9.0.41, 9.0.42, 9.0.43, 9.0.44, 9.0.45, 9.0.46@operato/headroom: 9.0.2, 9.0.35, 9.0.36, 9.0.37@operato/help: 9.0.35, 9.0.36, 9.0.37, 9.0.38, 9.0.39, 9.0.40, 9.0.41, 9.0.42, 9.0.43, 9.0.44, 9.0.45, 9.0.46@operato/i18n: 9.0.35, 9.0.36, 9.0.37@operato/input: 9.0.27, 9.0.35, 9.0.36, 9.0.37, 9.0.38, 9.0.39, 9.0.40, 9.0.41, 9.0.42, 9.0.43, 9.0.44, 9.0.45, 9.0.46, 9.0.47, 9.0.48@operato/layout: 9.0.35, 9.0.36, 9.0.37@operato/popup: 9.0.22, 9.0.35, 9.0.36, 9.0.37, 9.0.38, 9.0.39, 9.0.40, 9.0.41, 9.0.42, 9.0.43, 9.0.44, 9.0.45, 9.0.46, 9.0.49@operato/pull-to-refresh: 9.0.36, 9.0.37, 9.0.38, 9.0.39, 9.0.40, 9.0.41, 9.0.42@operato/shell: 9.0.22, 9.0.35, 9.0.36, 9.0.37, 9.0.38, 9.0.39@operato/styles: 9.0.2, 9.0.35, 9.0.36, 9.0.37@operato/utils: 9.0.22, 9.0.35, 9.0.36, 9.0.37, 9.0.38, 9.0.39, 9.0.40, 9.0.41, 9.0.42, 9.0.43, 9.0.44, 9.0.45, 9.0.46, 9.0.49@teselagen/bio-parsers: 0.4.30@teselagen/bounce-loader: 0.3.16, 0.3.17@teselagen/file-utils: 0.3.22@teselagen/liquibase-tools: 0.4.1@teselagen/ove: 0.7.40@teselagen/range-utils: 0.3.14, 0.3.15@teselagen/react-list: 0.8.19, 0.8.20@teselagen/react-table: 6.10.19, 6.10.20, 6.10.22@teselagen/sequence-utils: 0.3.34@teselagen/ui: 0.9.10@thangved/callback-window: 1.1.4@things-factory/attachment-base: 9.0.43, 9.0.44, 9.0.45, 9.0.46, 9.0.47, 9.0.48, 9.0.49, 9.0.50@things-factory/auth-base: 9.0.43, 9.0.44, 9.0.45@things-factory/email-base: 9.0.42, 9.0.43, 9.0.44, 9.0.45, 9.0.46, 9.0.47, 9.0.48, 9.0.49, 9.0.50, 9.0.51, 9.0.52, 9.0.53, 9.0.54@things-factory/env: 9.0.42, 9.0.43, 9.0.44, 9.0.45@things-factory/integration-base: 9.0.43, 9.0.44, 9.0.45@things-factory/integration-marketplace: 9.0.43, 9.0.44, 9.0.45@things-factory/shell: 9.0.43, 9.0.44, 9.0.45@tnf-dev/api: 1.0.8@tnf-dev/core: 1.0.8@tnf-dev/js: 1.0.8@tnf-dev/mui: 1.0.8@tnf-dev/react: 1.0.8@ui-ux-gang/devextreme-angular-rpk: 24.1.7@yoobic/design-system: 6.5.17@yoobic/jpeg-camera-es6: 1.0.13@yoobic/yobi: 8.7.53airchief: 0.3.1airpilot: 0.8.8angulartics2: 14.1.1, 14.1.2browser-webdriver-downloader: 3.0.8capacitor-notificationhandler: 0.0.2, 0.0.3capacitor-plugin-healthapp: 0.0.2, 0.0.3capacitor-plugin-ihealth: 1.1.8, 1.1.9capacitor-plugin-vonage: 1.0.2, 1.0.3capacitorandroidpermissions: 0.0.4, 0.0.5config-cordova: 0.8.5cordova-plugin-voxeet2: 1.0.24cordova-voxeet: 1.0.32create-hest-app: 0.1.9db-evo: 1.1.4, 1.1.5devextreme-angular-rpk: 21.2.8ember-browser-services: 5.0.2, 5.0.3ember-headless-form-yup: 1.0.1ember-headless-form: 1.1.2, 1.1.3ember-headless-table: 2.1.5, 2.1.6ember-url-hash-polyfill: 1.0.12, 1.0.13ember-velcro: 2.2.1, 2.2.2encounter-playground: 0.0.2, 0.0.3, 0.0.4, 0.0.5eslint-config-crowdstrike-node: 4.0.3, 4.0.4eslint-config-crowdstrike: 11.0.2, 11.0.3eslint-config-teselagen: 6.1.7, 6.1.8globalize-rpk: 1.7.4graphql-sequelize-teselagen: 5.3.8, 5.3.9html-to-base64-image: 1.0.2json-rules-engine-simplified: 0.2.1, 0.2.4jumpgate: 0.0.2koa2-swagger-ui: 5.11.1, 5.11.2mcfly-semantic-release: 1.3.1mcp-knowledge-base: 0.0.2mcp-knowledge-graph: 1.2.1mobioffice-cli: 1.0.3monorepo-next: 13.0.1, 13.0.2mstate-angular: 0.4.4mstate-cli: 0.4.7mstate-dev-react: 1.1.1mstate-react: 1.6.5ng2-file-upload: 7.0.2, 7.0.3, 8.0.1, 8.0.2, 8.0.3, 9.0.1ngx-bootstrap: 18.1.4, 19.0.3, 19.0.4, 20.0.3, 20.0.4, 20.0.5ngx-color: 10.0.1, 10.0.2ngx-toastr: 19.0.1, 19.0.2ngx-trend: 8.0.1ngx-ws: 1.1.5, 1.1.6oradm-to-gql: 35.0.14, 35.0.15oradm-to-sqlz: 1.1.2ove-auto-annotate: 0.0.9, 0.0.10pm2-gelf-json: 1.0.4, 1.0.5printjs-rpk: 1.6.1react-complaint-image: 0.0.32, 0.0.35react-jsonschema-form-conditionals: 0.3.18, 0.3.21react-jsonschema-form-extras: 1.0.4react-jsonschema-rxnt-extras: 0.4.9remark-preset-lint-crowdstrike: 4.0.1, 4.0.2rxnt-authentication: 0.0.3, 0.0.4, 0.0.5, 0.0.6rxnt-healthchecks-nestjs: 1.0.2, 1.0.3, 1.0.4, 1.0.5rxnt-kue: 1.0.4, 1.0.5, 1.0.6, 1.0.7swc-plugin-component-annotate: 1.9.1, 1.9.2tbssnch: 1.0.2teselagen-interval-tree: 1.1.2tg-client-query-builder: 2.14.4, 2.14.5tg-redbird: 1.3.1, 1.3.2tg-seq-gen: 1.0.9, 1.0.10thangved-react-grid: 1.0.3ts-gaussian: 3.0.5, 3.0.6ts-imports: 1.0.1, 1.0.2tvi-cli: 0.1.5ve-bamreader: 0.2.6, 0.2.7ve-editor: 1.0.1, 1.0.2verror-extra: 6.0.1voip-callkit: 1.0.2, 1.0.3wdio-web-reporter: 0.1.3yargs-help-output: 5.0.3yoo-styles: 6.0.326
Frequently asked questions
- Shai-Hulud is a supply chain campaign against npm packages, named after the YAML workflow file the malware writes into repositories. In September 2025 it compromised numerous packages published by the crowdstrike-publisher account and hundreds of third-party packages, including @ctrl/tinycolor and packages from the NativeScript ecosystem. A manipulated bundle.js steals secrets and uses GitHub Actions to gain a lasting foothold.
More articles

HTTP2Shell: the Brotli flaw reaches far beyond Node.js
HTTP2Shell is not a new flaw but CVE-2026-111497 in any software with a Brotli decoder. Who is affected, and why the version number misleads.
- 5 min read

Node2Shell: why patching Node alone is not enough
Node2Shell exploits a flaw in the Brotli decoder that Node.js bundles. The fix ships in Node 22.23.4, 24.22.1 and 26.12.1 – and in Brotli itself.
- 5 min read

Fortinet hardening release: patching without an advisory
Fortinet shipped critical fixes for FortiOS, FortiManager and FortiAnalyzer on 22 October 2026. The advisories with CVE ids only follow on 10 November.
- 5 min read
See your attack surface within 24 hours.
We set up your workspace and walk you through the first findings.
- 14 days free, all features
- No credit card required
- We walk you through your first findings