
External attack surface
Attack surface management from the attacker's view
blacklens.io discovers every internet-facing domain, IP, service and technology, scores each asset and reports changes before someone else exploits them.
- Technology Fingerprints
- 1000+
- Monitored Assets
- 1 Mio+
- top-level domains in lookalike detection
- 357
- product versions for technology matching
- 2.1M+
Every asset, including the forgotten ones
You provide a domain, an IP or a network. blacklens.io expands the scope on its own and finds hosts, services, web applications and technologies.
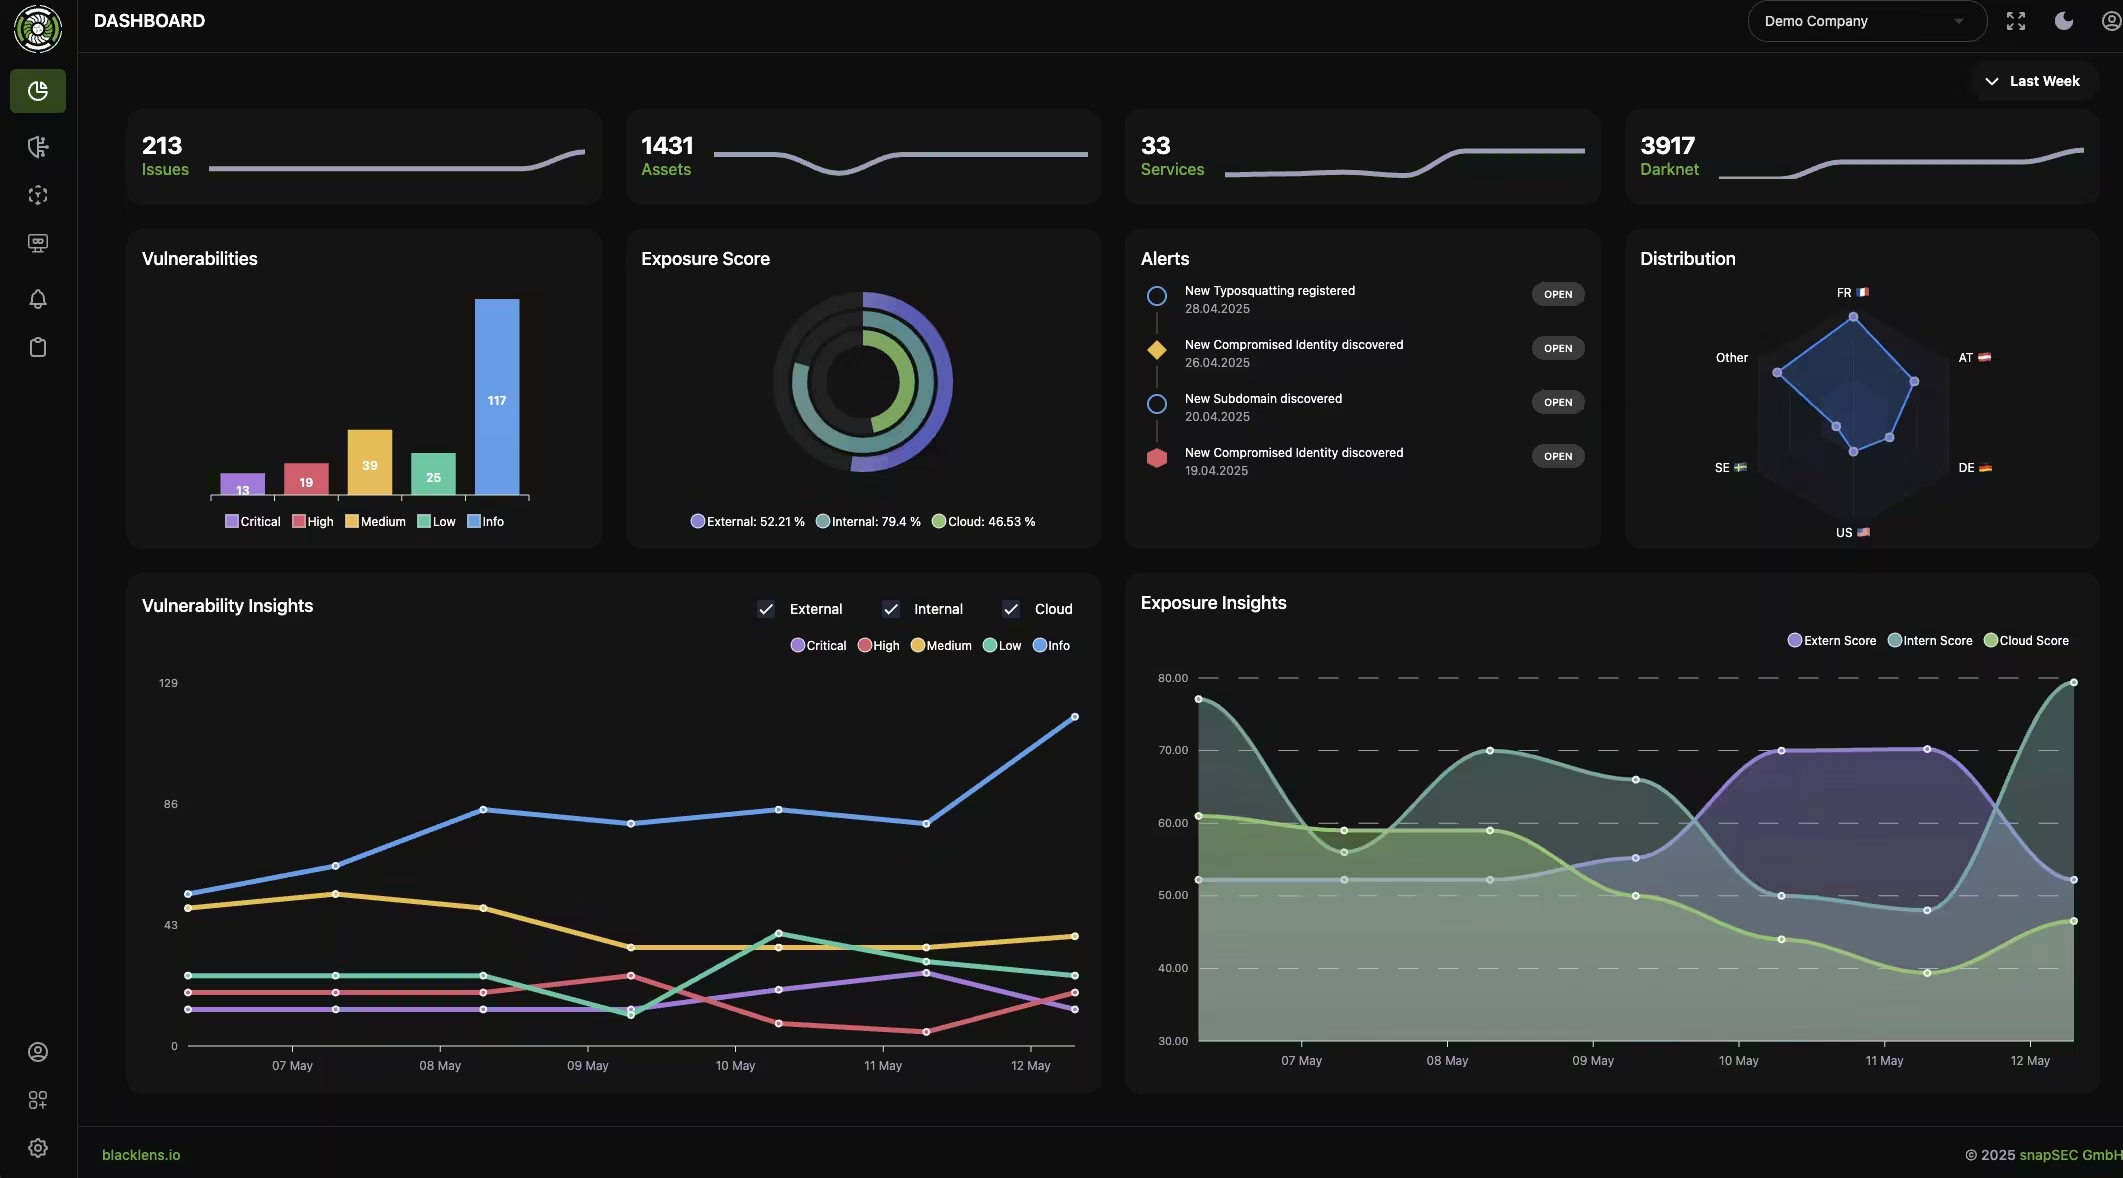
Visuals show sample data.
Discovery in five steps
Host, service, web, technology and lookalike, each step building on the one before.
Technology inventory as CPE
The basis for real-time CVE matching in the early warning system.
Tags and CSV export
Tag assets individually or in bulk and export any list as CSV.
Score it, don't just list it
A long asset list helps no one. blacklens.io shows what is exposed, vulnerable or not yet monitored.
Visuals show sample data.
Spot lookalike domains, prepare the takedown
Phishing often starts with a domain that resembles yours. blacklens.io checks spelling variants of your domains daily, takes screenshots and assesses every hit.
Visuals show sample data.
AI verdict with confidence
Impersonation, suspicious or parked, backed by signals such as a password field.
Pre-filled abuse report
Once five evidence criteria are met, you send it to the registrar or hosting provider.
The list stays current
Lookalikes that stay inconspicuous for 60 days are removed automatically.
Frequently asked questions
- External attack surface management (EASM) is the continuous, automated discovery of every system of a company that is reachable from the internet: domains, subdomains, IP addresses, open services, web applications and the technologies in use. Unlike a one-off scan, EASM runs continuously and reports changes such as new hosts, new services or expiring certificates. blacklens.io adds vulnerabilities, dark web signals and lookalike domains to that view so the inventory becomes a prioritised task list.
Related solutions
The capabilities on this page are building blocks. This is how customers use them day to day.
CTEM
Attack surface, prioritisation and remediation as a continuous five-phase process.
Unified Vulnerability Management
External, internal and cloud findings in one workflow with clear ownership.
Ransomware readiness
Close entry points at the perimeter before access brokers sell them.
Compliance & audit
Evidence for NIS2, ISO 27001 and cyber insurance from day-to-day operations.
See your attack surface within 24 hours.
Start with one domain. We set up the workspace and walk through the first findings with you.
- 14 days free, all features
- No credit card required
- We walk you through your first findings