
Dark web monitoring
Find leaked access before anyone uses it
Credentials, stealer logs and corporate access are traded long before an incident. blacklens.io finds hits for your domains, matches them against your accounts and tells you what to do.
Visuals show sample data.
- polling interval for ransomware leak sites
- ~30 min
- ransomware victims recorded since 2023
- 20,000+
- ransomware groups on watch
- 290+
- countries covered by leak-site monitoring
- 125+
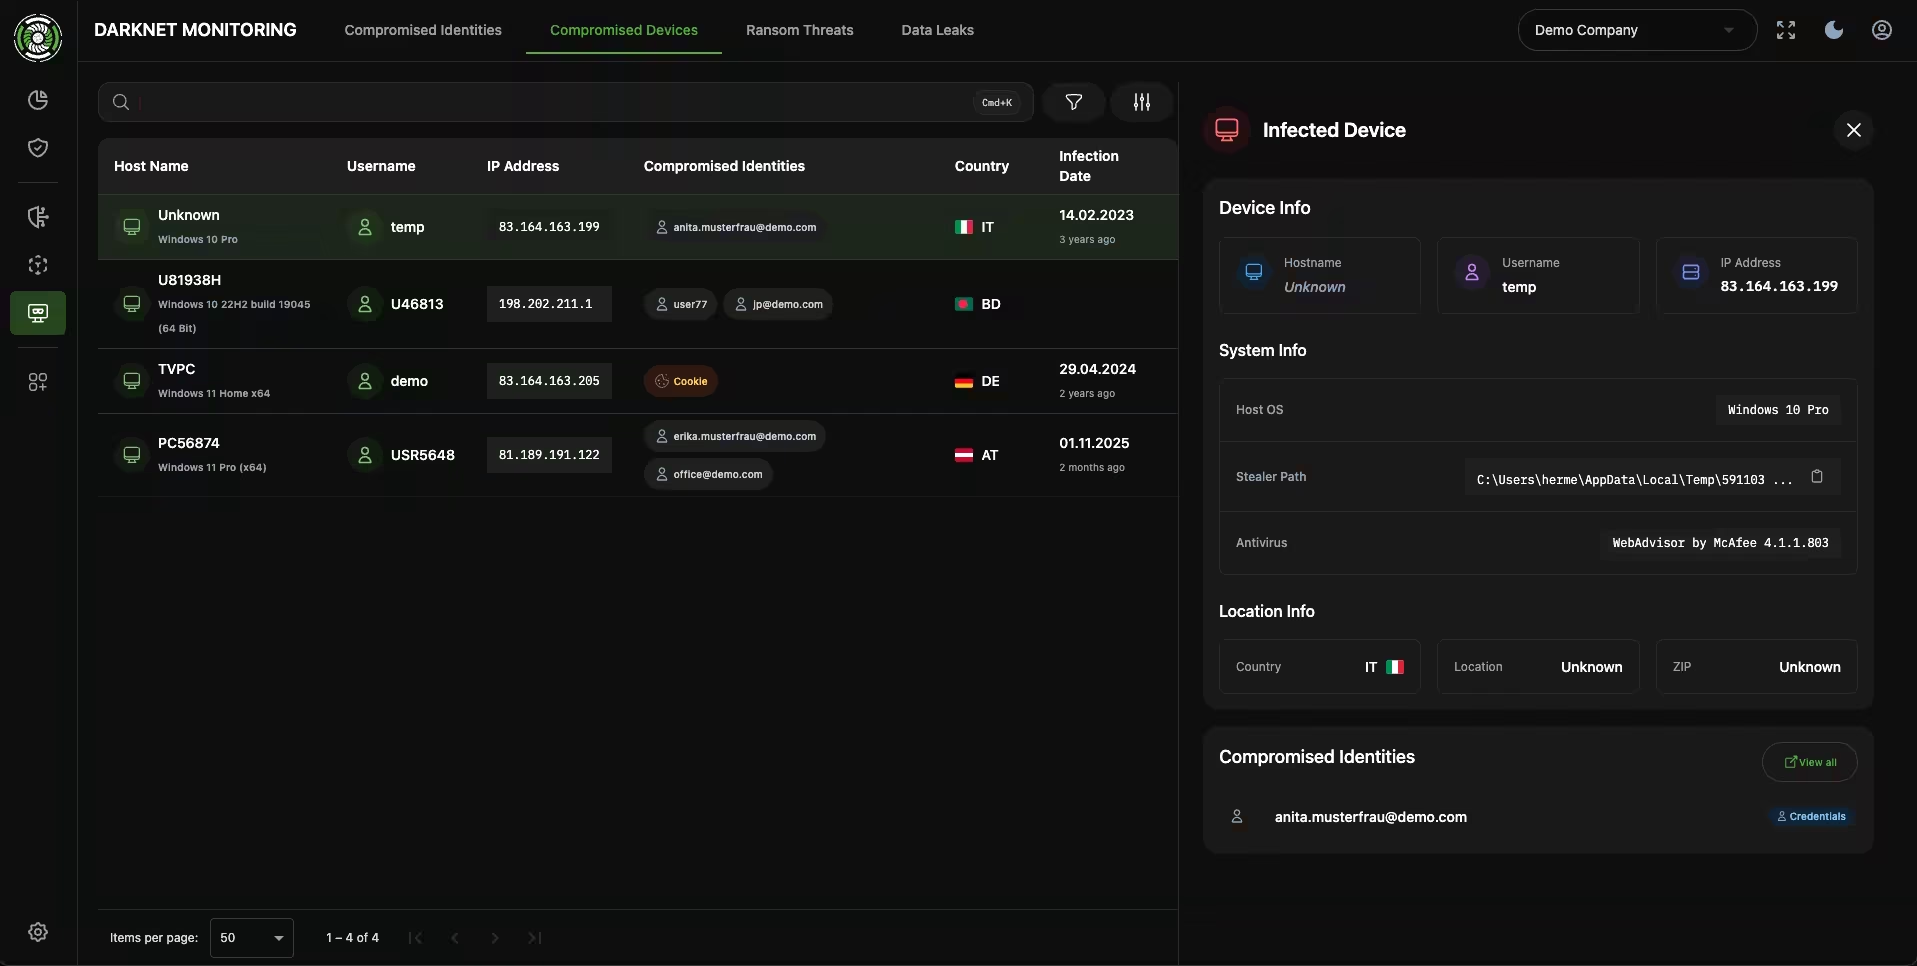
Compromised identities and devices
Credentials, session cookies and personal data for your domains, with source and infected device.
- IP address
- 198.51.100.23
- Country
- Austria
- Antivirus
- Microsoft Defender
- Infection
- 4 days ago
C:\Users\mhuber\AppData\Local\Temp\Visuals show sample data.
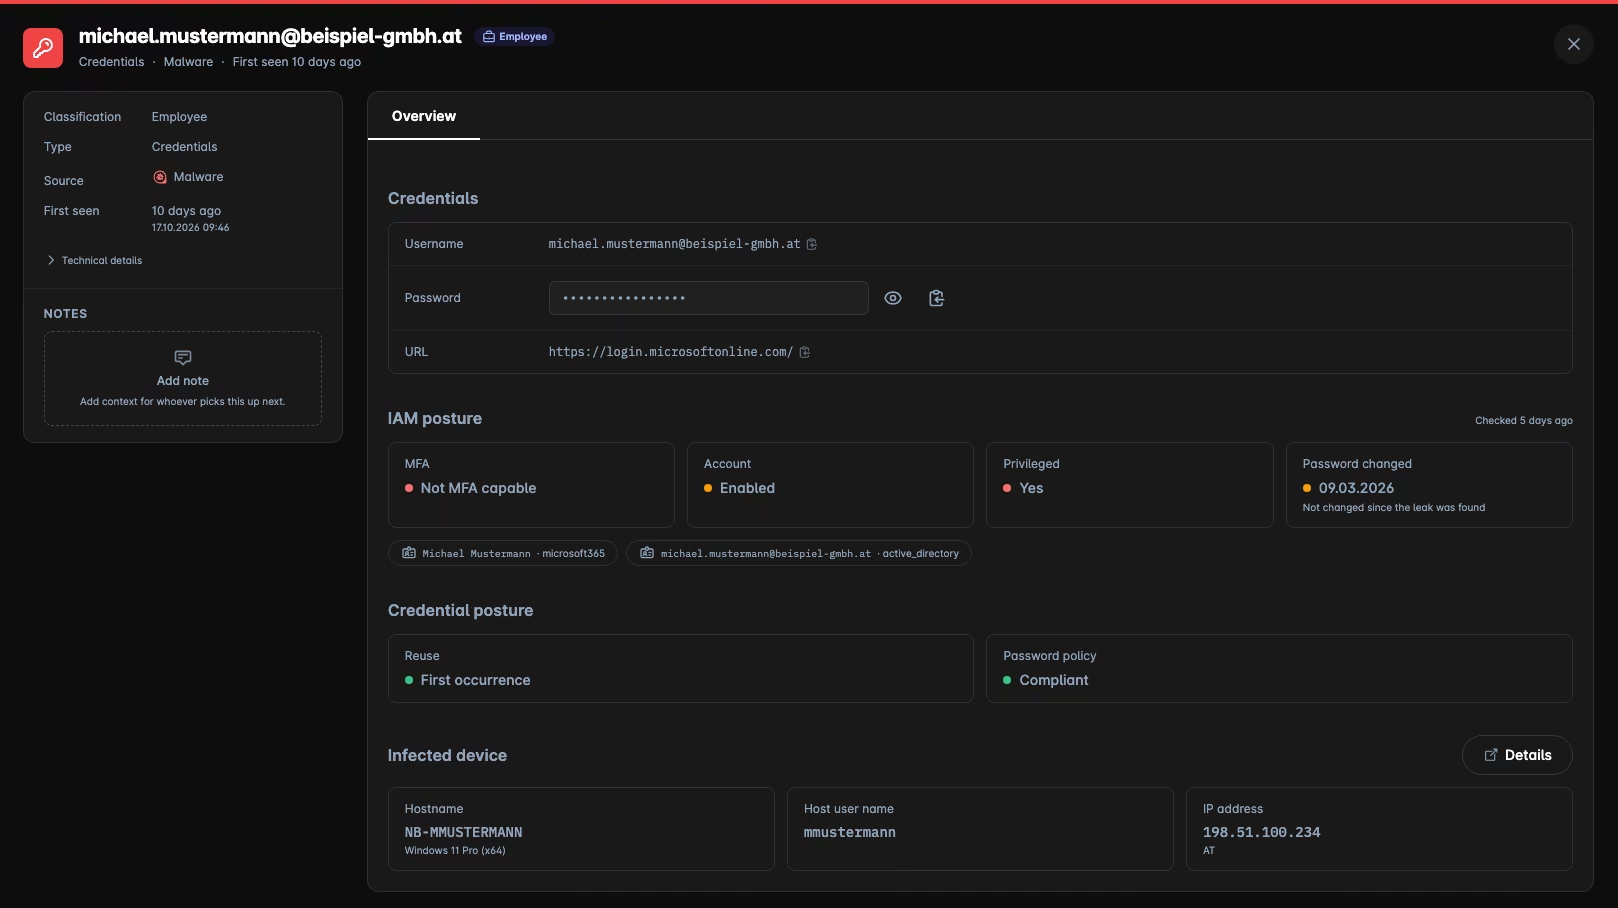
Every hit matched against your IAM inventory
blacklens.io matches every leaked username against the accounts in your IAM inventory: Microsoft 365 through the integration, Active Directory by email address from the Sentry AD scan. Missing data is never treated as safe.
Visuals show sample data.
Privileged accounts stand out
A directory role in Microsoft 365 or admin rights in AD flag the hit as privileged.
MFA and account status
For Microsoft 365 you see whether the account is MFA-capable and whether it is disabled.
Password changed since the leak?
The last password change is compared with the day blacklens.io recorded the leak.
Check leaked passwords against your policy
Set a minimum length, excluded terms such as your company name and required character classes, or write a regular expression. Every leaked cleartext password is checked against it.
Beispiel2026!Violates policyVisuals show sample data.
"Policy compliant" is a warning sign
A leaked password that meets your policy may still be in use.
Tested in your browser
The test field checks passwords in your browser. Nothing is sent or stored.
Known credentials
If the same username and password pair resurfaces, it is flagged without a second alert.
Spot ransomware attacks on your suppliers
Ransomware groups publish their victims on leak sites. blacklens.io matches new entries against your supplier watchlist and reports every hit. To see how secure a supplier is before an attack, use the supplier risk rating.
Visuals show sample data.
Ransomware leak sites
New victims recorded roughly every 30 minutes with threat actor, country and screenshot.
Supplier watchlist
Import your suppliers via CSV. A match raises the alert "Ransomware threat discovered".
From watchlist to rating
With "Monitor in Supply Chain", suppliers get a security grade from A to F every week.
From hit to response
A dark web hit is an alert like any other, with severity, owner and status. It reaches your team where they work.
Visuals show sample data.
Email, push and integrations
Policies by severity and type, via email, mobile app, Teams, Slack or Sentinel.
Next to your vulnerabilities
A leaked VPN password and a flaw in the VPN gateway appear side by side.
Exportable and auditable
CSV and PDF export, plus an activity log of who handled which hit and when.
Frequently asked questions
- Dark web monitoring (also darknet monitoring) watches underground forums and marketplaces, stealer logs, combolists and ransomware leak sites for data that belongs to your company: email addresses and passwords of your domains, session cookies, personal data, infected corporate devices and mentions of your suppliers. blacklens.io attributes every hit to employees or customers, matches it against your IAM inventory and turns it into an alert with a concrete recommendation.
Related solutions
The capabilities on this page are building blocks. This is how customers use them day to day.
Ransomware readiness
Close credentials and entry points before access brokers sell them.
Supplier risk rating
An A to F security grade for every supplier, re-rated every week.
Supply chain monitoring
Manage and evidence supply chain risk for NIS2 and DORA.
Cyber insurance
Evidence insurer requirements for monitoring and response.
Is your company already on the dark web?
14 days free. We set up monitoring for your domains and go through the first hits with you.
- 14 days free, all features
- No credit card required
- We walk you through your first findings