
Enterprise
Every subsidiary and site in one view
Subsidiaries, acquisitions and cloud accounts in one platform: a workspace per company, prioritised centrally and connected to your SIEM, ticketing and identity provider.
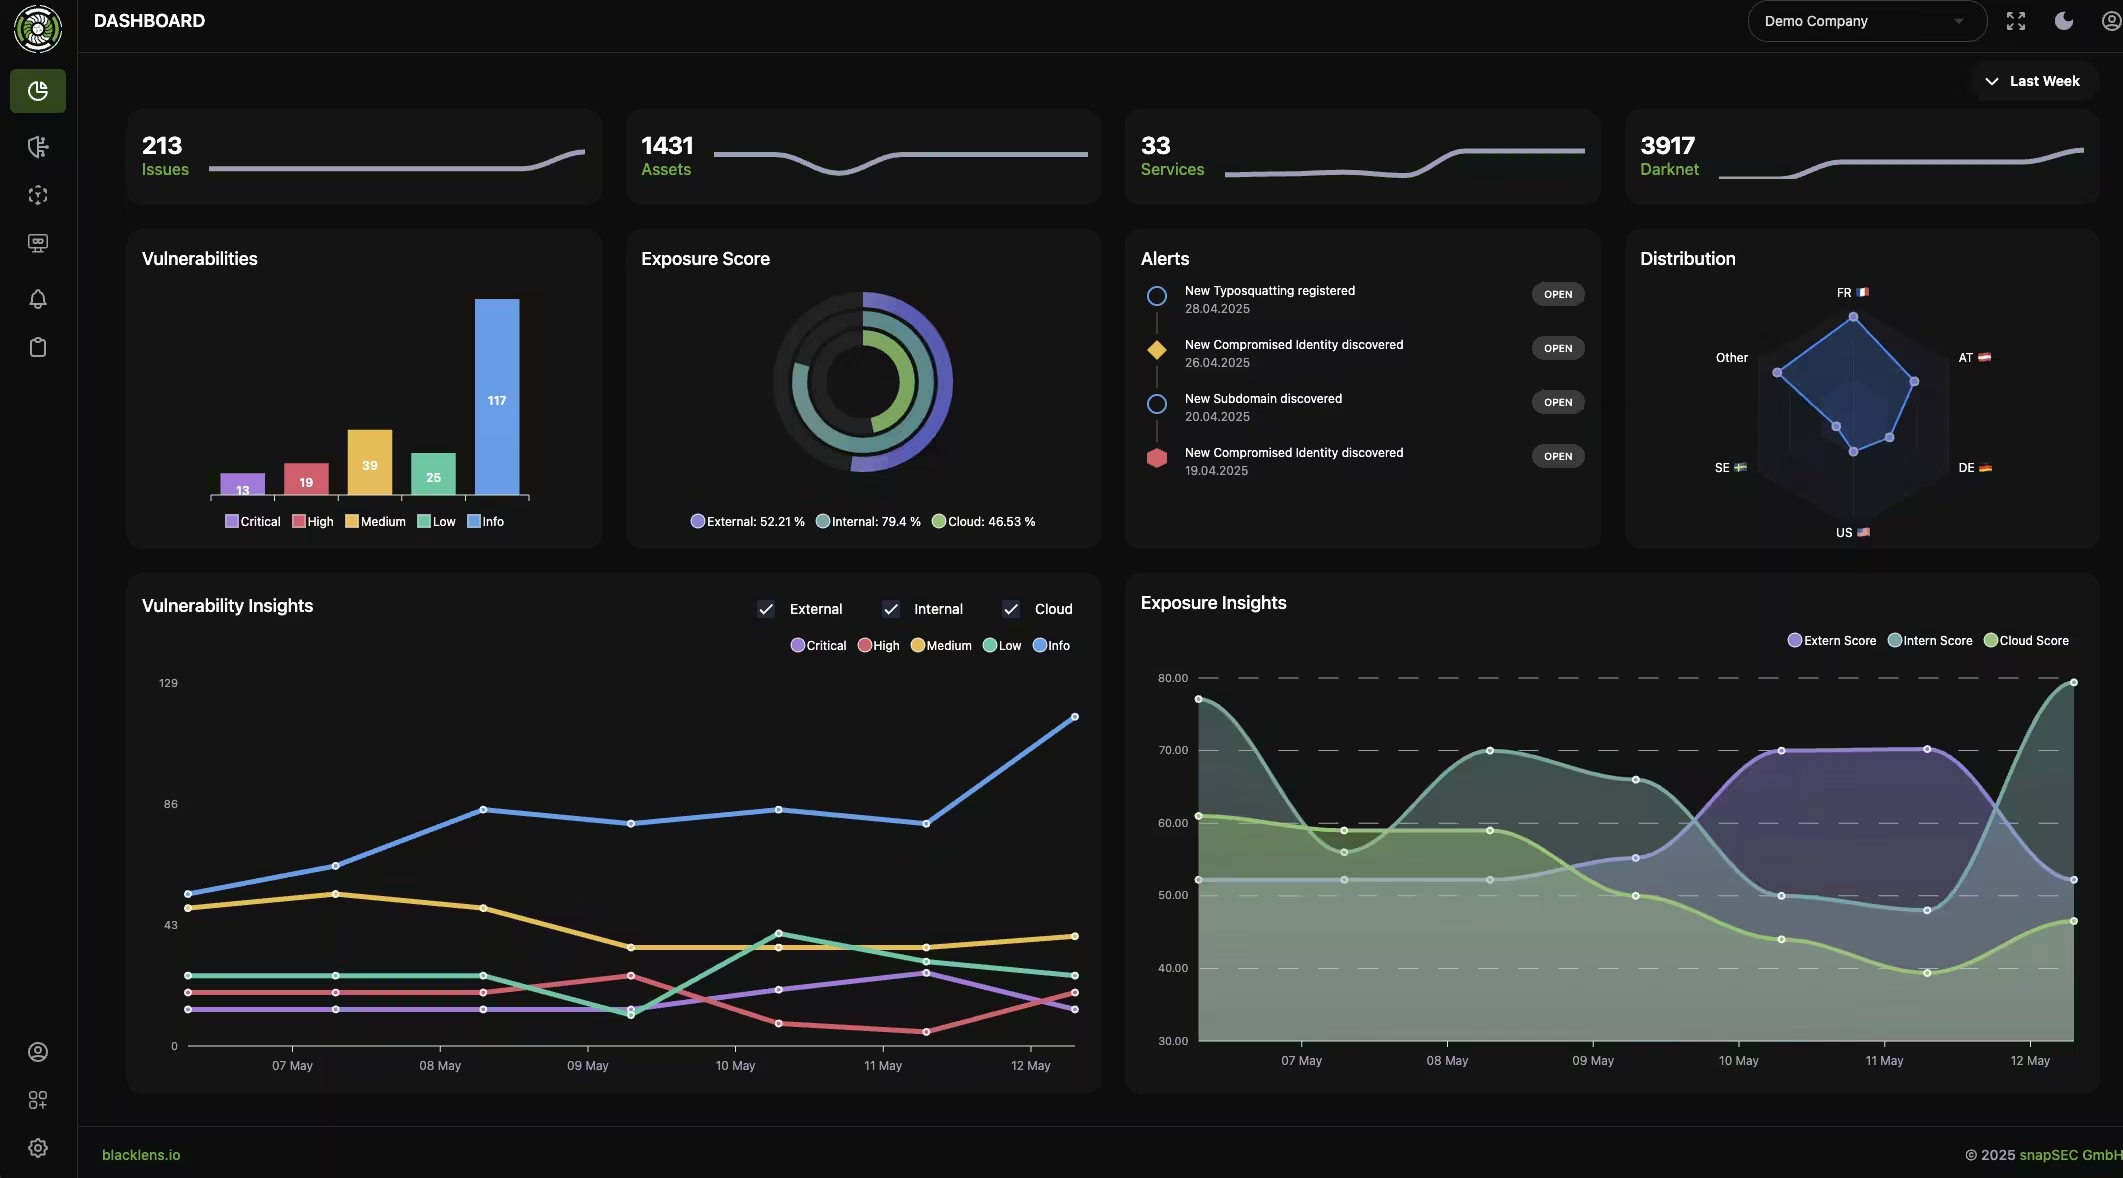
Large environments, distributed responsibility
Every company in the group runs its own IT, while attackers see one shared attack surface.
Grown structures
Subsidiaries, sites and acquisitions with their own IT and service providers.
Unknown networks
IP ranges and domains from projects and acquisitions are missing from every inventory.
Tools without context
Scanners, cloud consoles and threat feeds deliver raw data in separate silos.
Evidence for regulators and customers
NIS2, DORA, ISO 27001 and customer audits require provable processes.
A platform that mirrors your group structure
Steer centrally, own locally: each company sees its own findings, group IT sees them all.
Visuals show sample data.
Including the networks nobody remembers
Scope suggestions from RIPE data, threat intelligence and connected cloud accounts surface IP ranges and domains from acquisitions and old projects. Internally, Sentry scans every site.
Visuals show sample data.
Scope suggestions
New networks and domains to approve, instead of manual lists.
Sentry per site
As a VM or Docker container, unlimited agents, including OT and Active Directory.
Technology inventory
New CVEs matched in real time against the inventory of every company.
Evidence for the board, regulators and audit
Scheduled reports per company, a supplier watchlist checked against ransomware leak sites and pentests on an agreed schedule: evidence for NIS2, DORA and ISO 27001.
Visuals show sample data.
Executive report per company
Exposure score with trend, scheduled by email.
Supply chain in view
Supplier watchlist via CSV, matched against ransomware leak sites.
Pentests on your schedule
Weekly to yearly per target, with retest and report.
How the rollout works
- 1
Demo
Map your structure
We show the platform with your domains and plan workspaces, roles and integrations.
- 2
Pilot
One company first
14 days with full functionality, your external attack surface from day one.
- 3
Rollout
Company by company
More workspaces, SSO, Sentry per site, alerts in your SIEM and ticketing.
- Permissions across system and custom roles
- 53
- Endpoints in the REST API
- 250+
- Integrations, incl. Sentinel and Elastic
- 15
- Hosts per Sentry agent, unlimited agents
- 2,500
Used by manufacturers, retailers, software companies and IT service providers across the DACH region.


Frequently asked questions
- Through a tenant and its workspaces. Each company or site gets its own workspace with its own scope, modules, reports and notification policies. Group IT sees every workspace in the portfolio dashboard, while local teams only see their own through their role. AI features are also enabled per workspace.
Let us plan your structure together
In a demo we show workspaces, roles, SSO and the SIEM connection, using your own domains. Then you start with one company as a pilot.
- 14 days free, all features
- No credit card required
- We walk you through your first findings