Supply Chain Monitoring
Rate your suppliers before they become your risk
The supplier risk rating gives every supplier an outside-in security grade from A to F, re-rated weekly. A grade drop or severe new findings raise an alert. Your supplier does not have to do anything.
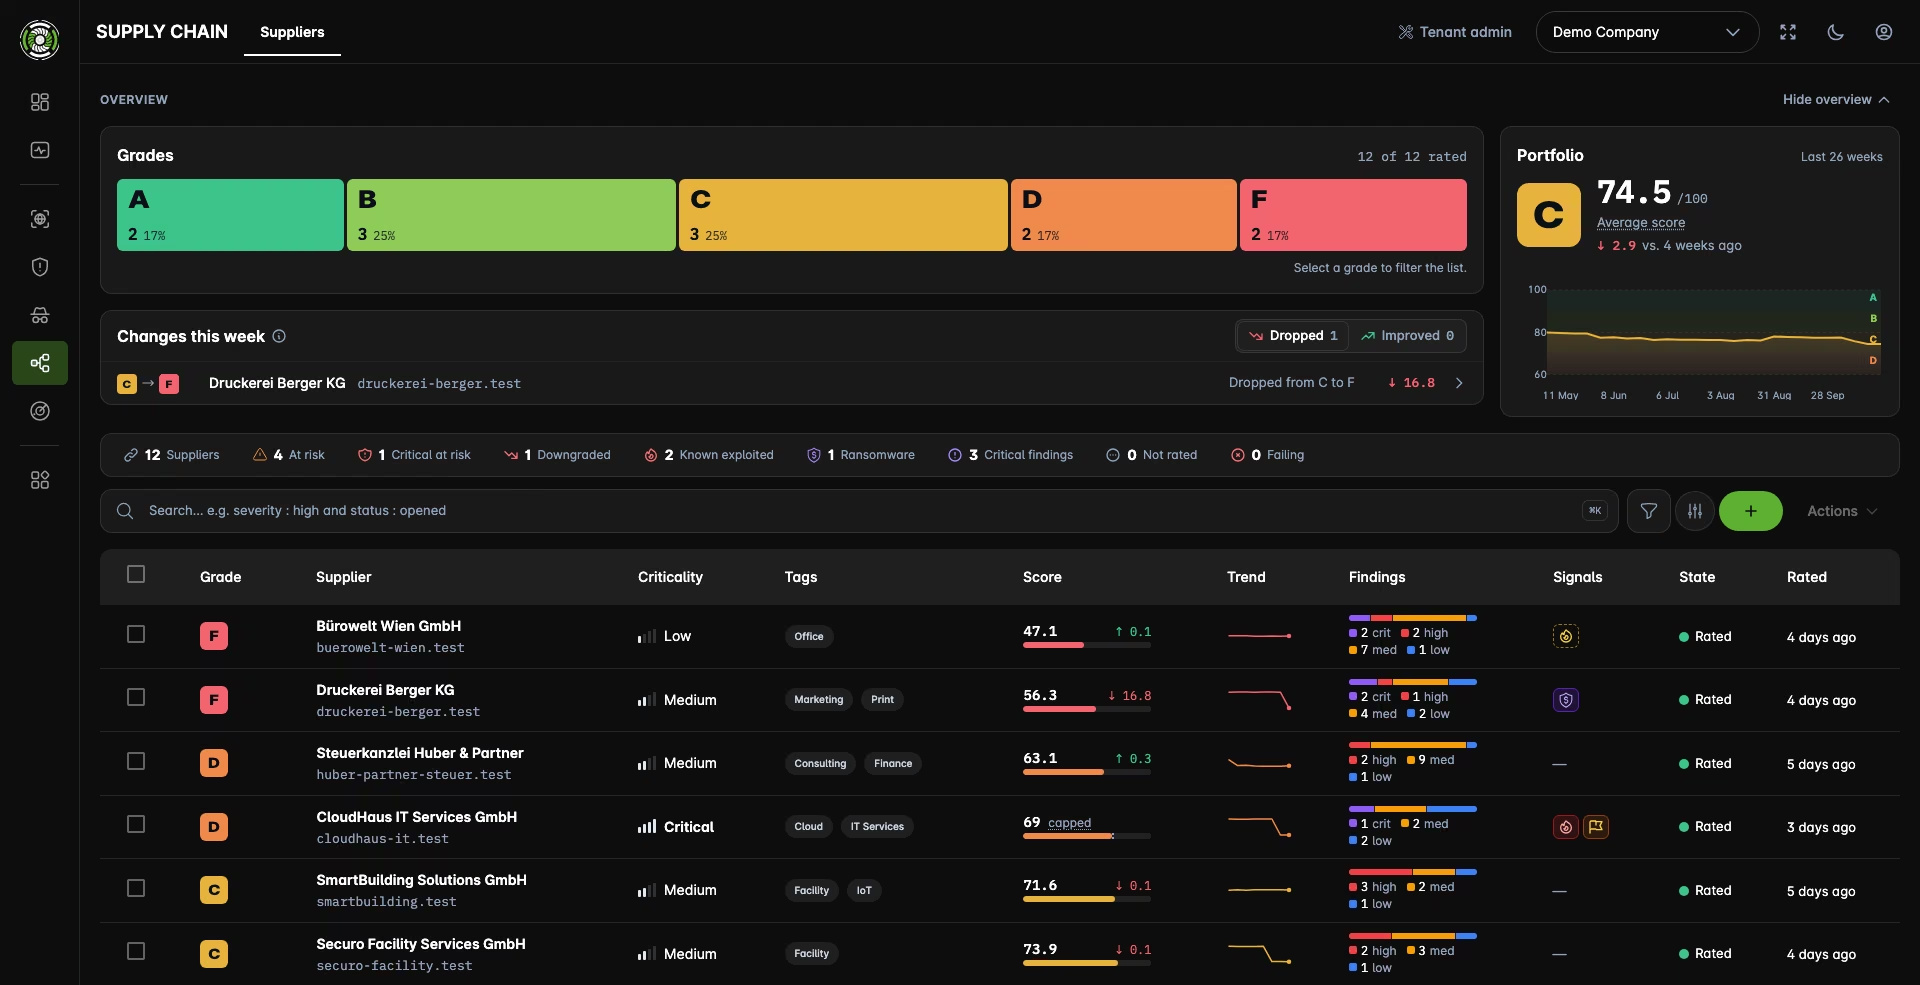
Visuals show sample data.
- security grade per supplier, score 0 to 100
- A–F
- rating areas, from patching to hosting
- 9
- until the automatic re-rating
- 7 days
- suppliers per workspace included in the licence
- 5
How the grade is made
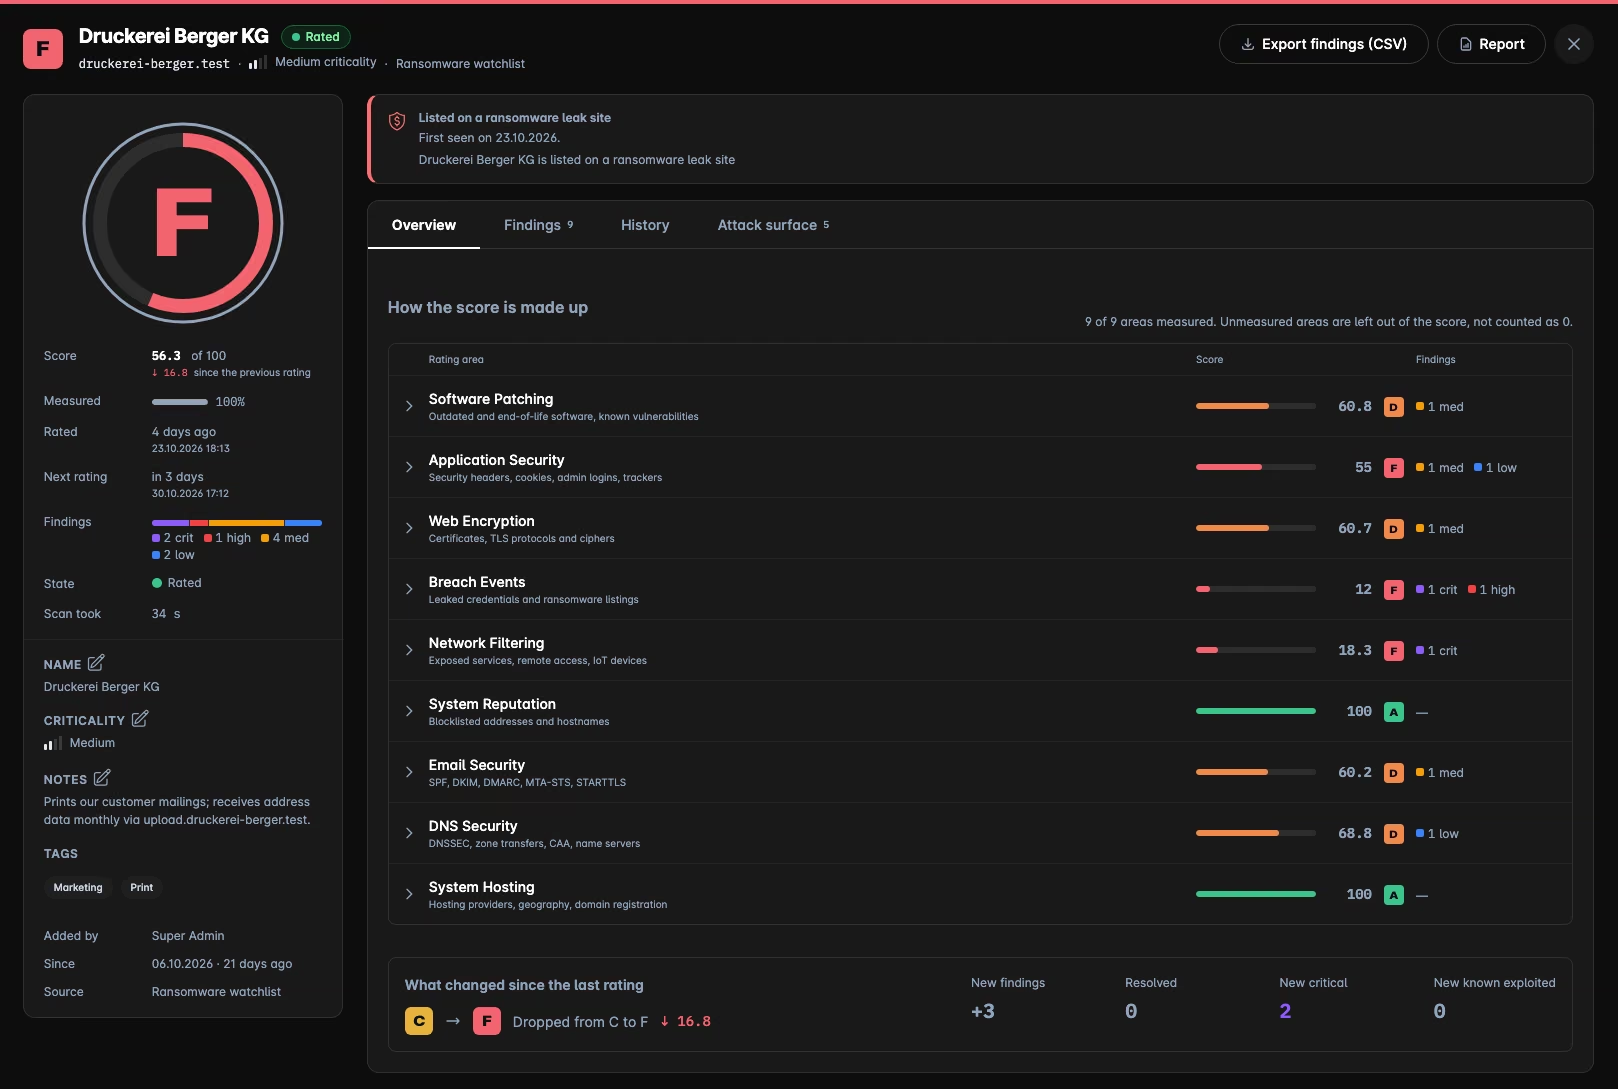
Every supplier gets a grade from A to F and a score from 0 to 100 across nine rating areas. A severe finding caps the score; areas that cannot be measured are left out rather than counted as zero.
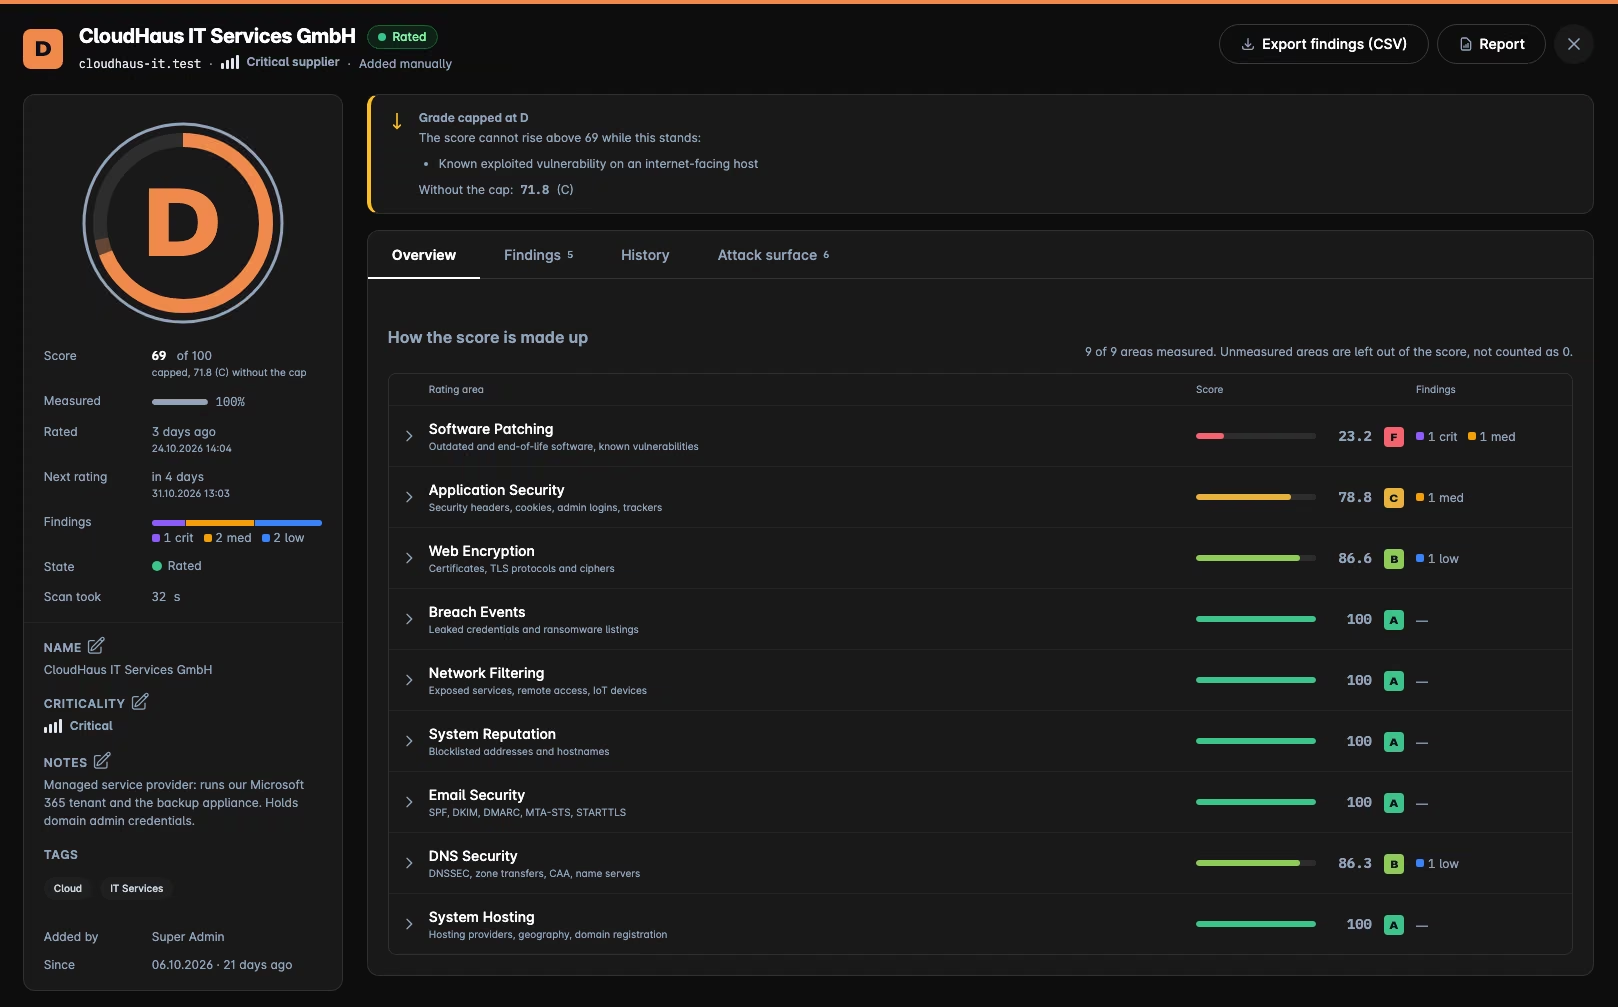
Visuals show sample data.
Software patching
Outdated and end-of-life software, known vulnerabilities.
Application security
Security headers, cookies, admin logins and trackers.
Web encryption
Certificates, TLS protocols and ciphers.
Breach events
Leaked credentials and ransomware leak-site listings.
Network filtering
Exposed services, remote access and IoT devices.
System reputation
Blocklisted addresses and hostnames.
Email security
SPF, DKIM, DMARC, MTA-STS and STARTTLS.
DNS security
DNSSEC, zone transfers, CAA and name servers.
System hosting
Hosting providers, geography and domain registration.
From the portfolio to the single finding
See at a glance which suppliers are slipping, then go straight to the finding that pulls the grade down.
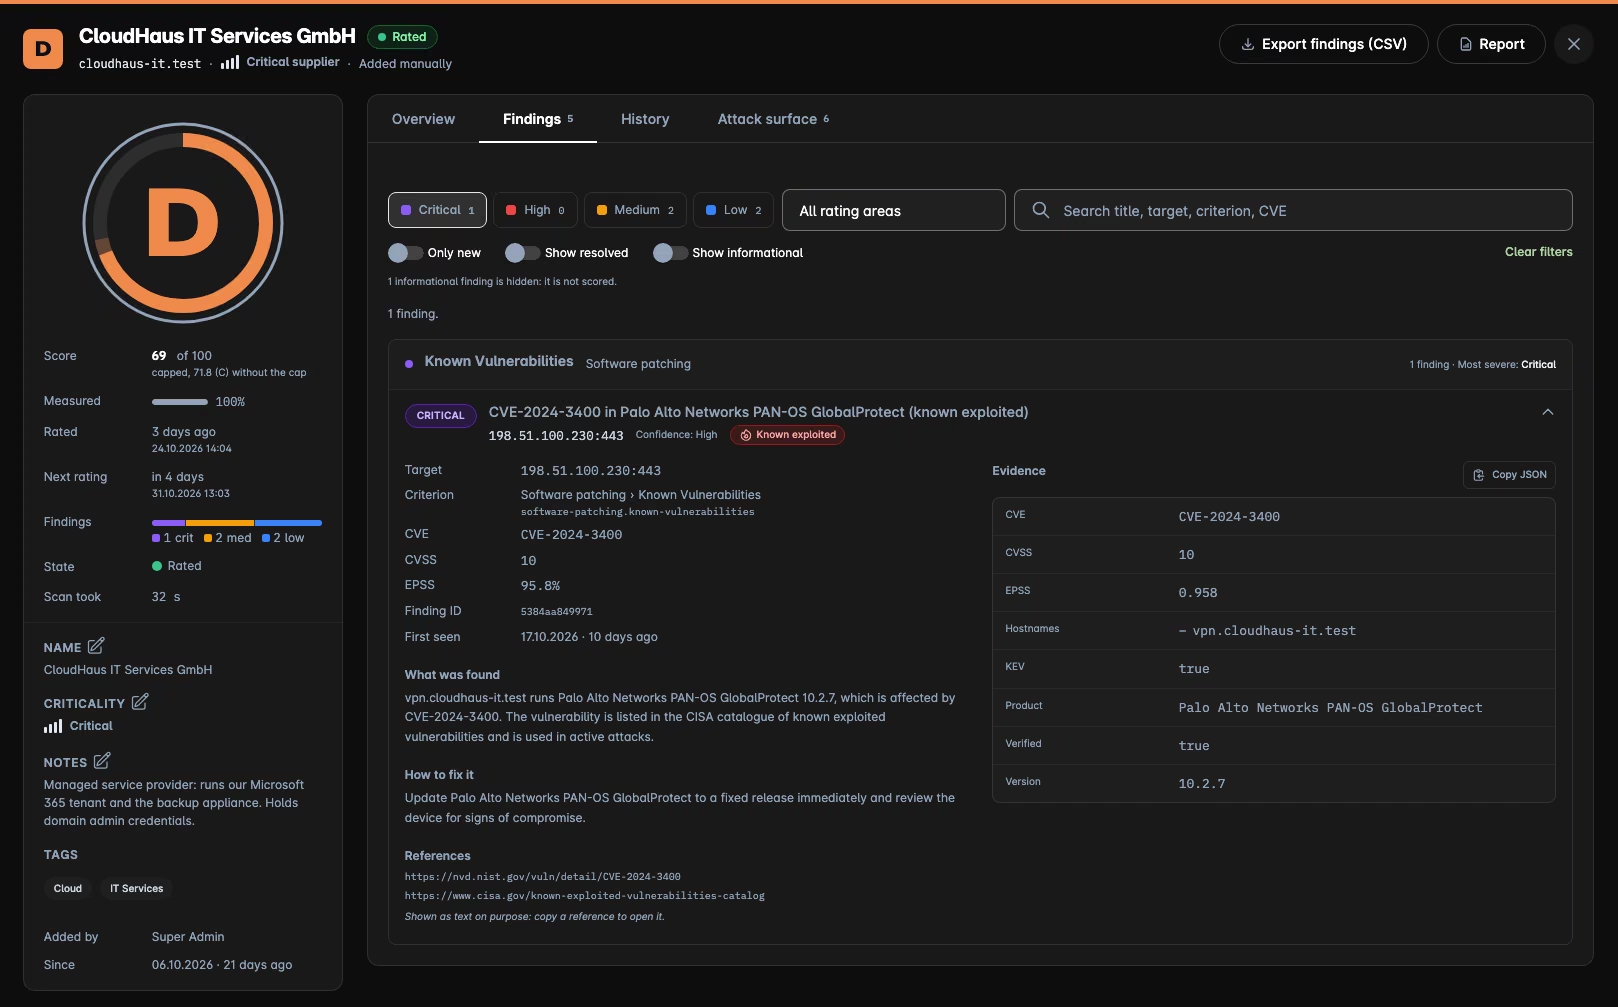
The alert contains only the supplier's domain
criticality = critical and kev_findings > 0Visuals show sample data.
Two layers: before an incident and after it
The rating shows a supplier's risk before anything happens. The ransomware watchlist reports the supplier when it appears on a leak site after an attack.
Visuals show sample data.
Rating before an incident
Grade, score and findings show every week where a supplier is exposed.
Watchlist after an attack
Ransomware leak sites are checked against your watchlist about every 30 minutes.
From watchlist to rating
“Monitor in Supply Chain” hands watchlist domains over to the rating.
Frequently asked questions
- A supplier risk rating is a security rating of a company you depend on, measured from the outside, the way an attacker sees it. blacklens.io checks nine areas: software patching, application security, web encryption, breach events, network filtering, system reputation, email security, DNS security and system hosting. The result is a grade (A, B, C, D or F), a score from 0 to 100 and a list of findings with remediation guidance. If too little can be measured, the grade shows N/A.
Related solutions
The capabilities on this page are building blocks. This is how customers use them day to day.
Supply chain monitoring
Manage supply chain risk for NIS2 and DORA with ratings and the ransomware watchlist.
NIS2
Evidence supply chain security under Art. 21 (2) d with technical data.
DORA
Keep a technical view of ICT third-party providers under Art. 28 to 30.
ISO 27001
Back supplier relationships under A.5.19 to A.5.22 with evidence.
See where your suppliers are exposed.
Rate your first suppliers in the 14-day trial: five suppliers per workspace are included.
- 14 days free, all features
- No credit card required
- We walk you through your first findings