
Solutions
Continuous Threat Exposure Management (CTEM)
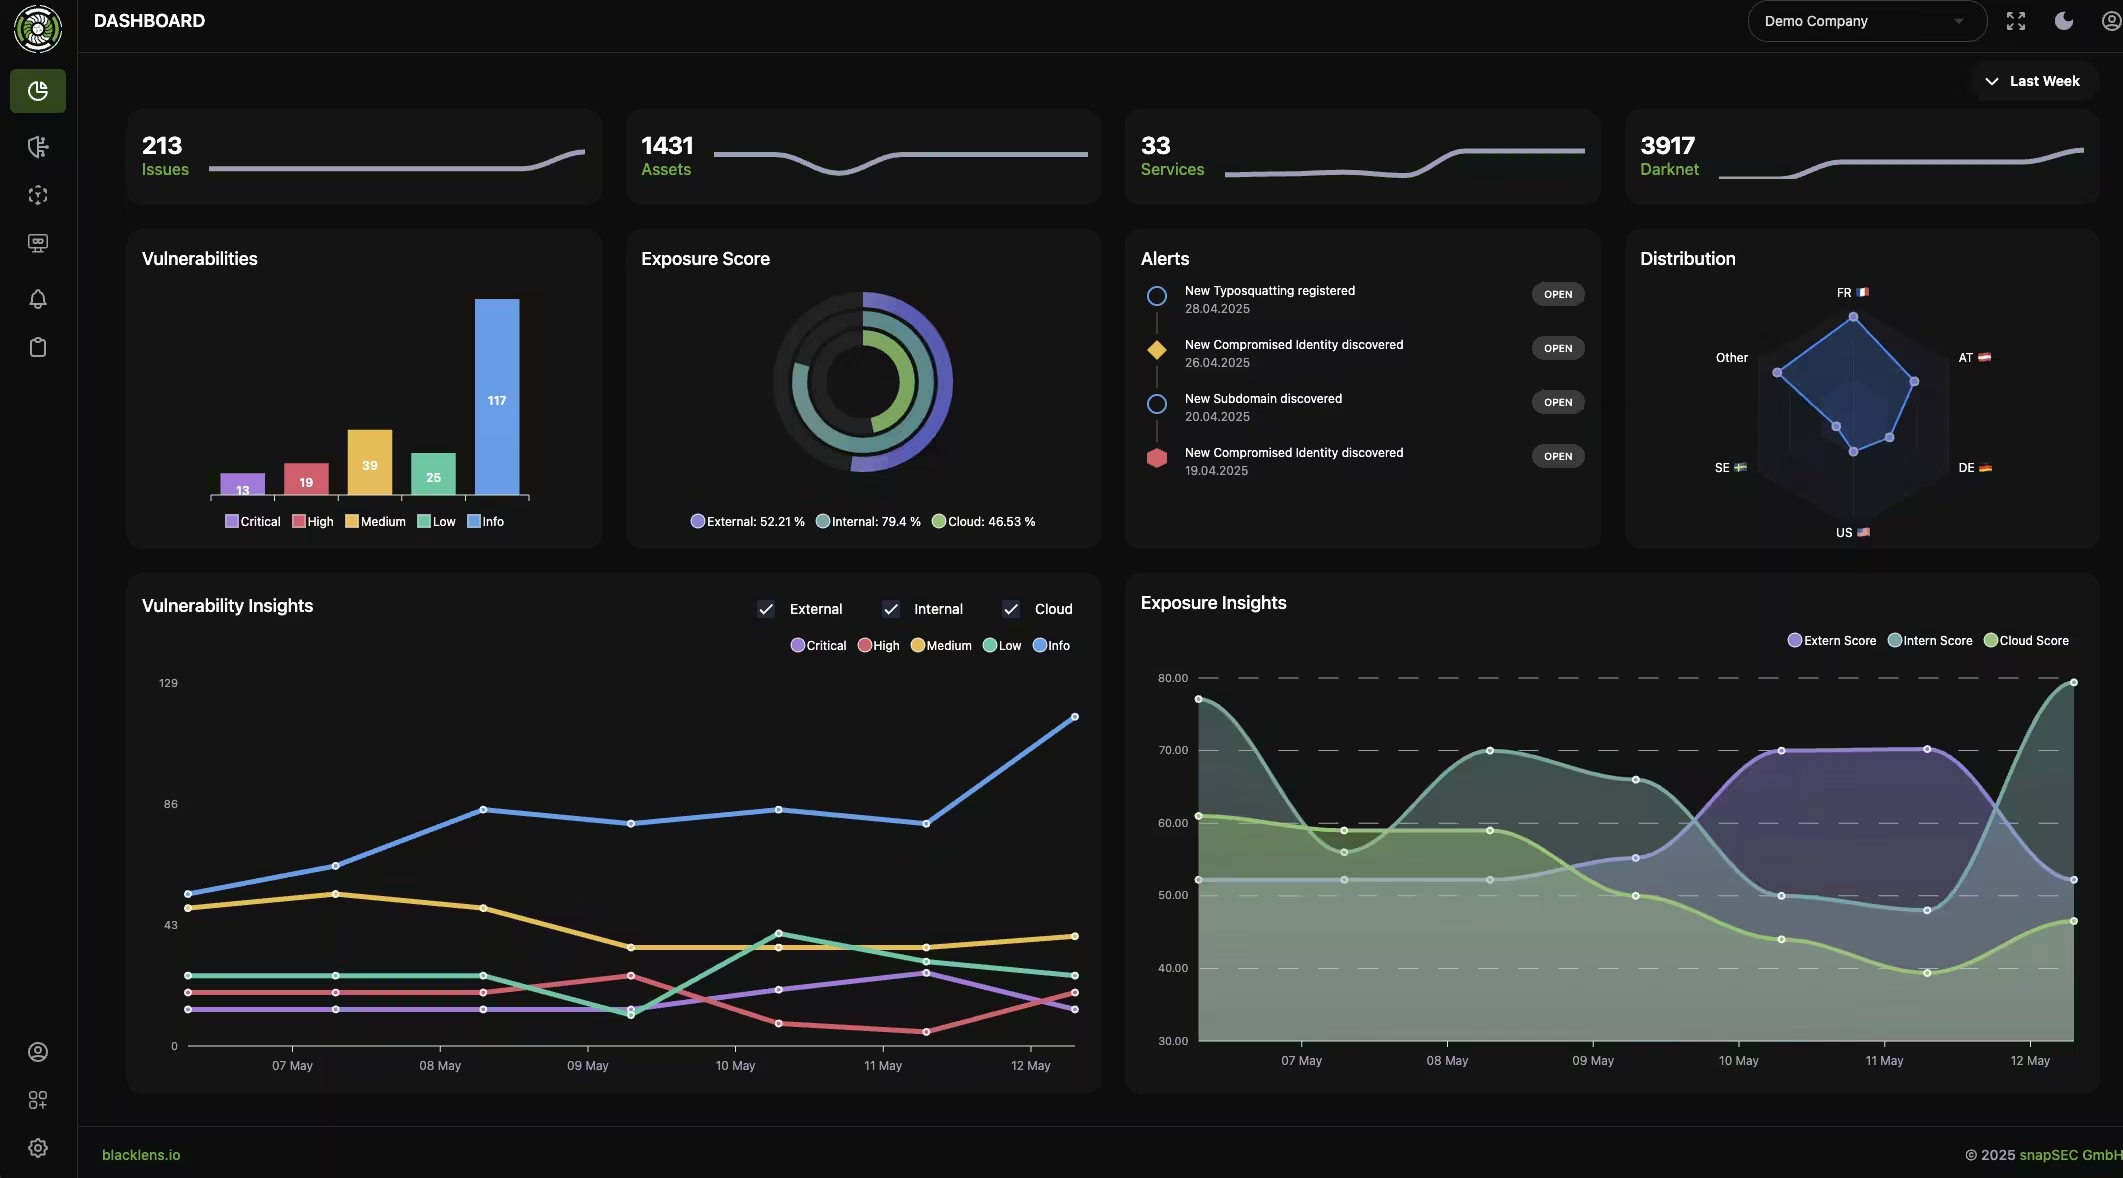
CTEM is a programme described by Gartner in which you continuously map, assess and reduce your attack surface. blacklens.io provides the data for all five phases.
Why point-in-time assessments fall short
Snapshots instead of a process
New risks appear with every deployment, every cloud account and every leaked password.
Separate tools
External, internal, cloud and dark web findings sit in separate lists. Nobody sees the whole picture.
CVSS without context
A CVSS score does not tell you whether an exploit exists or the system is reachable.
No follow-through
Without status, retest and history you cannot measure whether security work has an effect.
- vulnerability tests, updated daily
- 200,000+
- matching of new CVEs against your inventory
- real time
- ransomware victims tracked since 2023
- 20,000+
- cloud providers with configuration audit
- 6
The five phases of the CTEM cycle
Every round makes the attack surface smaller and the prioritisation sharper.
- 1
Scoping
Decide which external, internal and cloud systems are monitored continuously.
- 2
Discovery
Find vulnerabilities, misconfigurations and leaked credentials within the scope.
- 3
Prioritisation
Handle the exposures that are reachable and actually exploitable first.
- 4
Validation
Confirm prioritised findings technically and remove false positives.
- 5
Mobilisation
Hand actions to the responsible teams and track them until they are fixed.
How blacklens.io supports each phase
One platform for the whole cycle, with no data exports between phases.
- CVE published08:12
- 2 assets in your inventory affected09:00
- Confirmed by PoC scan09:26
- Alert sent to Microsoft Teams09:27
- Assigned to IT operations
- Update installed
- Re-scan confirmed: closed automatically
Visuals show sample data.
One cycle, one platform
Scope, findings, prioritisation and workflow interlock without data exports. The platform is hosted in ISO 27001 and SOC 2 certified data centres in the DACH region and the scanners run only in Austria, Germany and Switzerland.
Complete visibility
External, cloud and internal in one inventory.
Continuous detection
Automated, not just during scheduled assessments.
Prioritisation with context
EPSS, CISA KEV and exploit availability instead of plain CVSS.
Measurable improvement
Exposure score, trends and scheduled reports.
Frequently asked questions
- Continuous threat exposure management (CTEM) is a programme described by Gartner in which organisations continuously map, assess and reduce their attack surface instead of checking security once a year. Its focus is not the individual vulnerability but the exposure: everything an attacker can actually reach and exploit from outside or inside. CTEM shortens the time between an exposure appearing and being fixed, because that window decides whether an attacker gets in.
See CTEM in practice
Start with your domains and see within 24 hours which exposures blacklens.io finds.
- 14 days free, all features
- No credit card required
- We walk you through your first findings