
Solutions
Supply chain monitoring: detect partner risk early
Supply chain monitoring makes supplier risk visible. blacklens.io rates your suppliers from A to F every week and alerts you when one of them appears on a ransomware leak site.
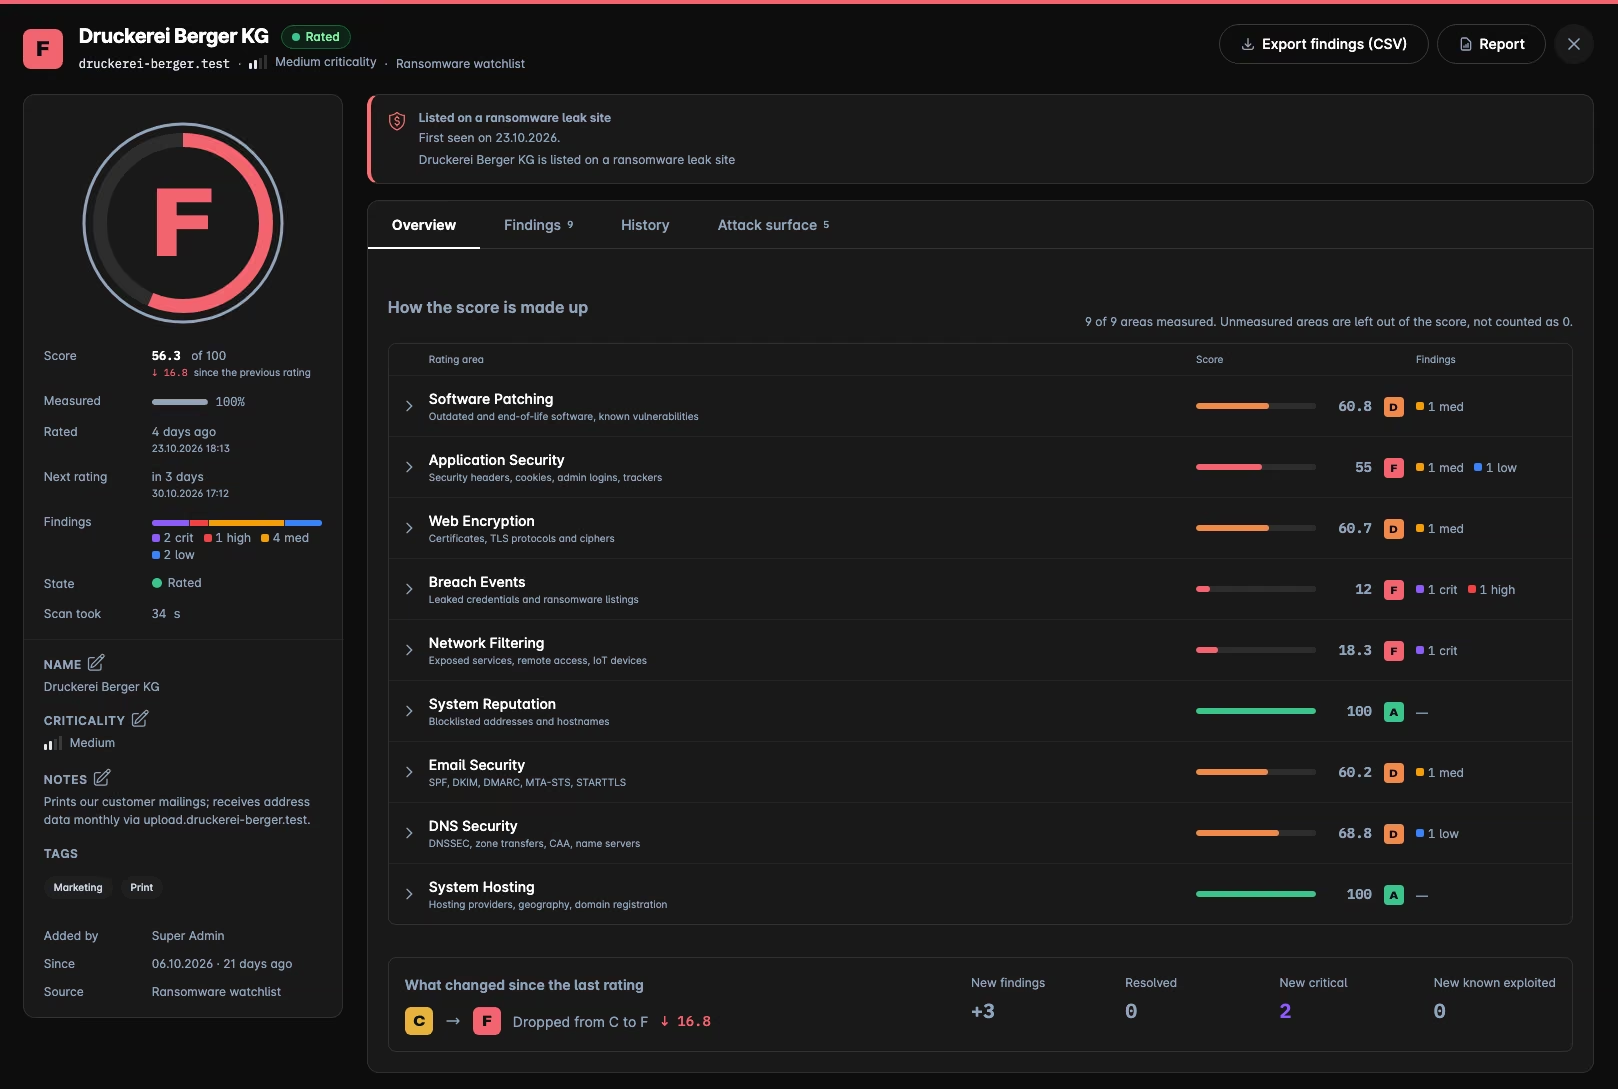
Visuals show sample data.
Challenges in modern supply chains
No view of third-party security
You usually only know from a partner's own statements how well it patches and secures its systems.
Compromised providers with access
A provider with remote access whose accounts are traded on the dark web leads straight into your network.
Late information
Whether a partner is compromised, you often learn weeks later from the supplier itself.
Regulatory requirements
NIS2, DORA and ISO 27001 require documented, ongoing monitoring of the supply chain.
How blacklens.io monitors your supply chain
The rating shows weak suppliers before an incident, the watchlist reports them after an attack. Dark web findings and new CVEs complete the picture.
- CVE published08:12
- 2 assets in your inventory affected09:00
- Confirmed by PoC scan09:26
- Alert sent to Microsoft Teams09:27
Visuals show sample data.
A monitored supply chain in four steps
- 1
Import suppliers
Add suppliers as a list or CSV, or take them over straight from the ransomware watchlist.
- 2
Rate and match
Suppliers are re-rated every seven days, and the watchlist is checked about every 30 minutes.
- 3
Alert on change
"Supplier risk increased" when a rating gets worse, "Ransomware threat discovered" on a leak site match.
- 4
File the evidence
The Supply Chain Report goes to ISMS and procurement on a schedule, and the rating history stays traceable.
Example from practice
Machinery manufacturer secures its supplier platform
blacklens.io found a partner's publicly reachable development environment with a valid access token for production APIs, plus a leaked IT service provider account on the dark web.
Result: The customer reacted within hours, before any damage occurred.
Evidence for NIS2, DORA and ISO 27001
Rating history, Supply Chain Report, alert history and activity log document how you monitor your suppliers and react to changes.
Visuals show sample data.
Frequently asked questions
- Supply chain monitoring is the regular observation of a company's digital dependencies: IT service providers, cloud providers, software vendors and technical subcontractors whose compromise directly affects your own security. The goal is to see weaknesses at partners before an incident and to learn about an incident from your own alerting system, not from the press. NIS2 (Article 21(2)(d)), DORA (ICT third-party risk) and ISO 27001 (A.5.19 to A.5.22) demand exactly this view of the supply chain.
Which of your suppliers slipped this week?
See the grade, findings and ransomware listings for your key suppliers in the 14-day trial.
- 14 days free, all features
- No credit card required
- We walk you through your first findings