Multi-tenant platform for MSSPs and IT service providers
Offer attack surface management, vulnerability management and dark web monitoring as your own service: separated by tenant, with your logo and via API.
Security services for dozens of customers, without a separate toolchain per customer.
Clean tenant separation
Scope, findings and reports separated per customer, in the API too.
Roles per service level
Customers only see reports or run their workspace themselves.
Automation
API, integrations and scheduled reports instead of manual work.
The tenant model: tenant, workspace, role
You see all tenants; your customer sees their workspace.
Backoffice3 workspaces
IIndustrie Muster AGTenantYour logo
Linz plant192.0.2.0/24ASMSentry
Salesshop.beispiel-gmbh.atASMDarknetAI on
Cloud accountsAWS, Microsoft 365CloudAI on
Users and roles8 roles plus custom
AAnalyst, partner SOCSSO via Microsoft Entra IDAll workspaces
HHead of IT, customerSSO via GoogleCustom role: reports only
PPentesterMFA enabledPentester role
50 permissionsCustom roles
Integrationsalerts, tickets, cloud
Jira
Microsoft Teams
Slack
GitHub
GitLab
Elastic
AWS
Microsoft Azure
Google Cloud
Cloudflare
Hetzner
Webhook
REST API250+ endpoints
Penetration testmanually validated
Authentication can be bypassedportal.beispiel-gmbh.atVerified
Other users' records readable via APIapi.beispiel-gmbh.atRetest passed
No limit on login attemptsshop.beispiel-gmbh.atUnder review
Tools for operating many customers
Which customer needs attention today?
Reportsscheduled by email
PDFExecutive reportWeekly, Monday 07:00
PDFVulnerability reportMonthly
PDFPentest reportAfter every test
Management, head of IT
Scheduled customer reports
Executive, vulnerability and pentest reports per customer, scheduled by email.
Workspace health3 notices
Sentry offlineHandel Nord GmbH, for 18 minOffline
Scan failedKanzlei Beispiel, today, 06:00Failed
3 open scope suggestionsIndustrie Muster AGOpen
Integrations onlineGemeinde MusterdorfOK
Health per workspace
Offline Sentries, failed scans and open scope suggestions at a glance.
Global alert recipientsall tenants
Compromised identity on the dark webIndustrie Muster AG, 08:14Critical
New CVE affects inventoryHandel Nord GmbH, 07:52High
Forwarded toHigh and above
SOC mailboxJiraMicrosoft Sentinel
Global alert recipients
Alerts from all tenants also in your SOC mailbox, ticketing or SIEM.
Security SnapshotPDF preview
beispiel-gmbh.atProspect
47Assets
112Services
6critical
Details lockedCritical
Details lockedHigh
Unlock the full report
Security Snapshot for prospects
A free preview of a prospect's attack surface, details locked.
Visuals show sample data.
Services partners build on blacklens.io
System houses sell vulnerability management as a service, MSSPs add dark web monitoring to their SOC. Blue Shield Security, itself an MSSP, is a reference customer.
Continuous inventory of the external attack surface, monthly report.
Managed vulnerability management
External and internal, with ticket handover and retest.
Dark web monitoring as a service
Compromised identities and leak site hits with a recommendation.
Compliance reporting
Evidence for NIS2, ISO 27001 and insurers.
Frequently asked questions
By active users (users with an active mailbox) for dark web monitoring and by assets (domains, subnets, IP addresses, cloud resources, Sentry assets). Two models are offered: a VAR model in which you resell licences, and an MSSP model in which you offer your own services on the platform. Details are on the partner page.
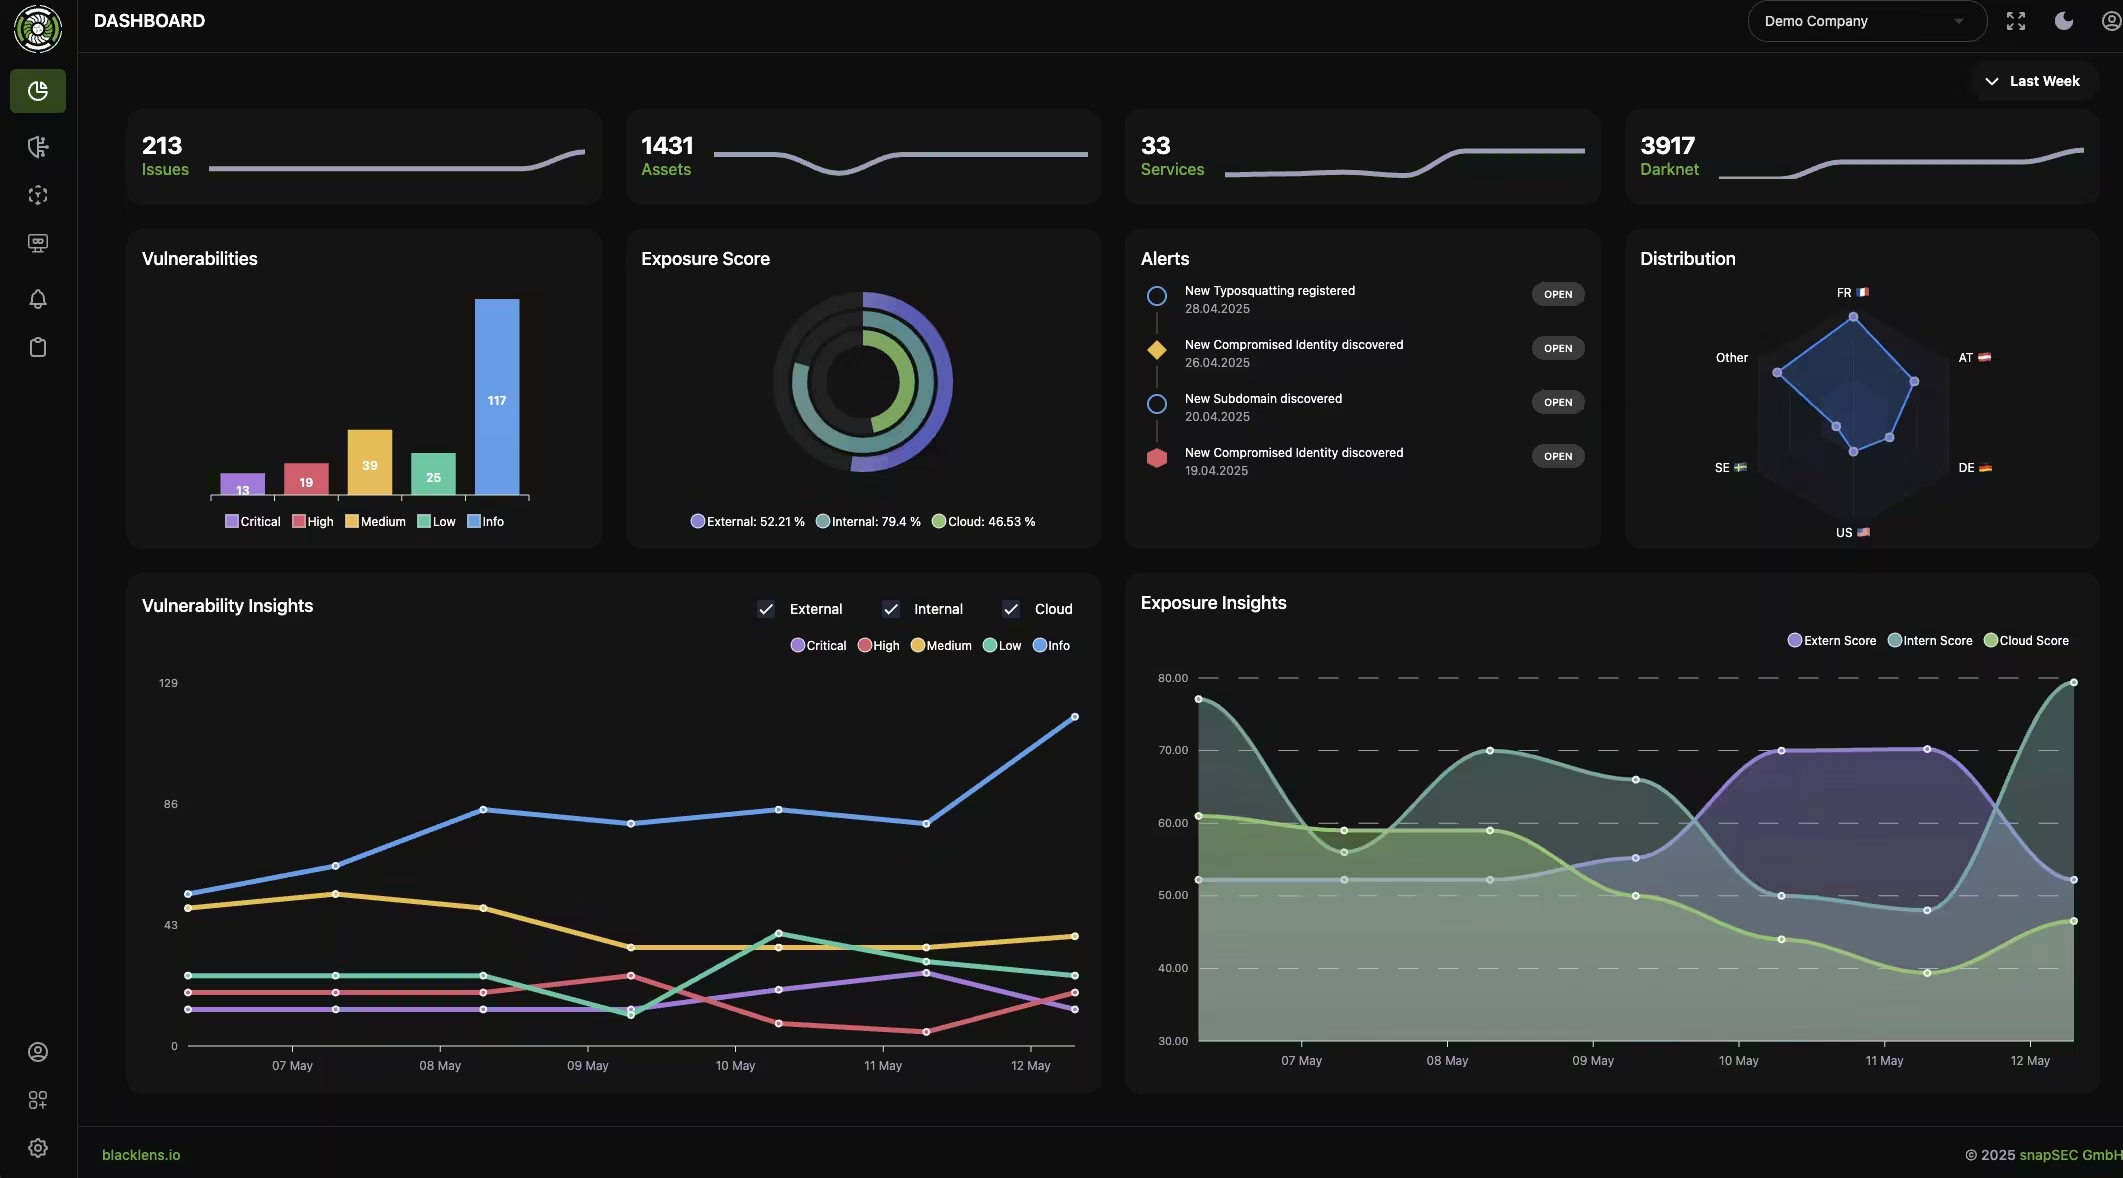
The portfolio dashboard summarises all workspaces of a partner on one page: exposure score, open critical findings and health status per customer, so you see which customer needs attention today. The backoffice console adds central management of tenants, workspaces, users, pentesters and Sentry agents, including your white-label logo as tenant branding.
Yes, if you want them to. Through roles you decide whether a customer only sees reports, may comment on findings or operates the workspace themselves. Equally, you can manage the customer entirely and only send them the scheduled reports. Customer accounts sign in via SSO with Microsoft Entra ID or Google, or with MFA.
Tenants are logically separated; every API call carries the tenant context, and API keys are always used together with the tenant. The platform is hosted in ISO 27001 and SOC 2 certified data centres in the DACH region, the scan infrastructure is located exclusively in Austria, Germany and Switzerland, and the AI runs as a self-hosted LLM without external providers.
You deploy Sentry as a VM or Docker container in the customer's network and enrol it with a one-time token in their workspace. Sentry scans servers, clients, network devices, OT components and Active Directory. The number of agents is unlimited; offline Sentries are reported after 15 minutes. Five Sentry assets are included per workspace.
Yes. After a live demo, partners receive their own access. For winning new customers, the "Security Snapshot" report generates a free preview of a prospect's attack surface with locked details. The commercial side, that is the VAR and MSSP models, licensing and onboarding, is described on the partner page.