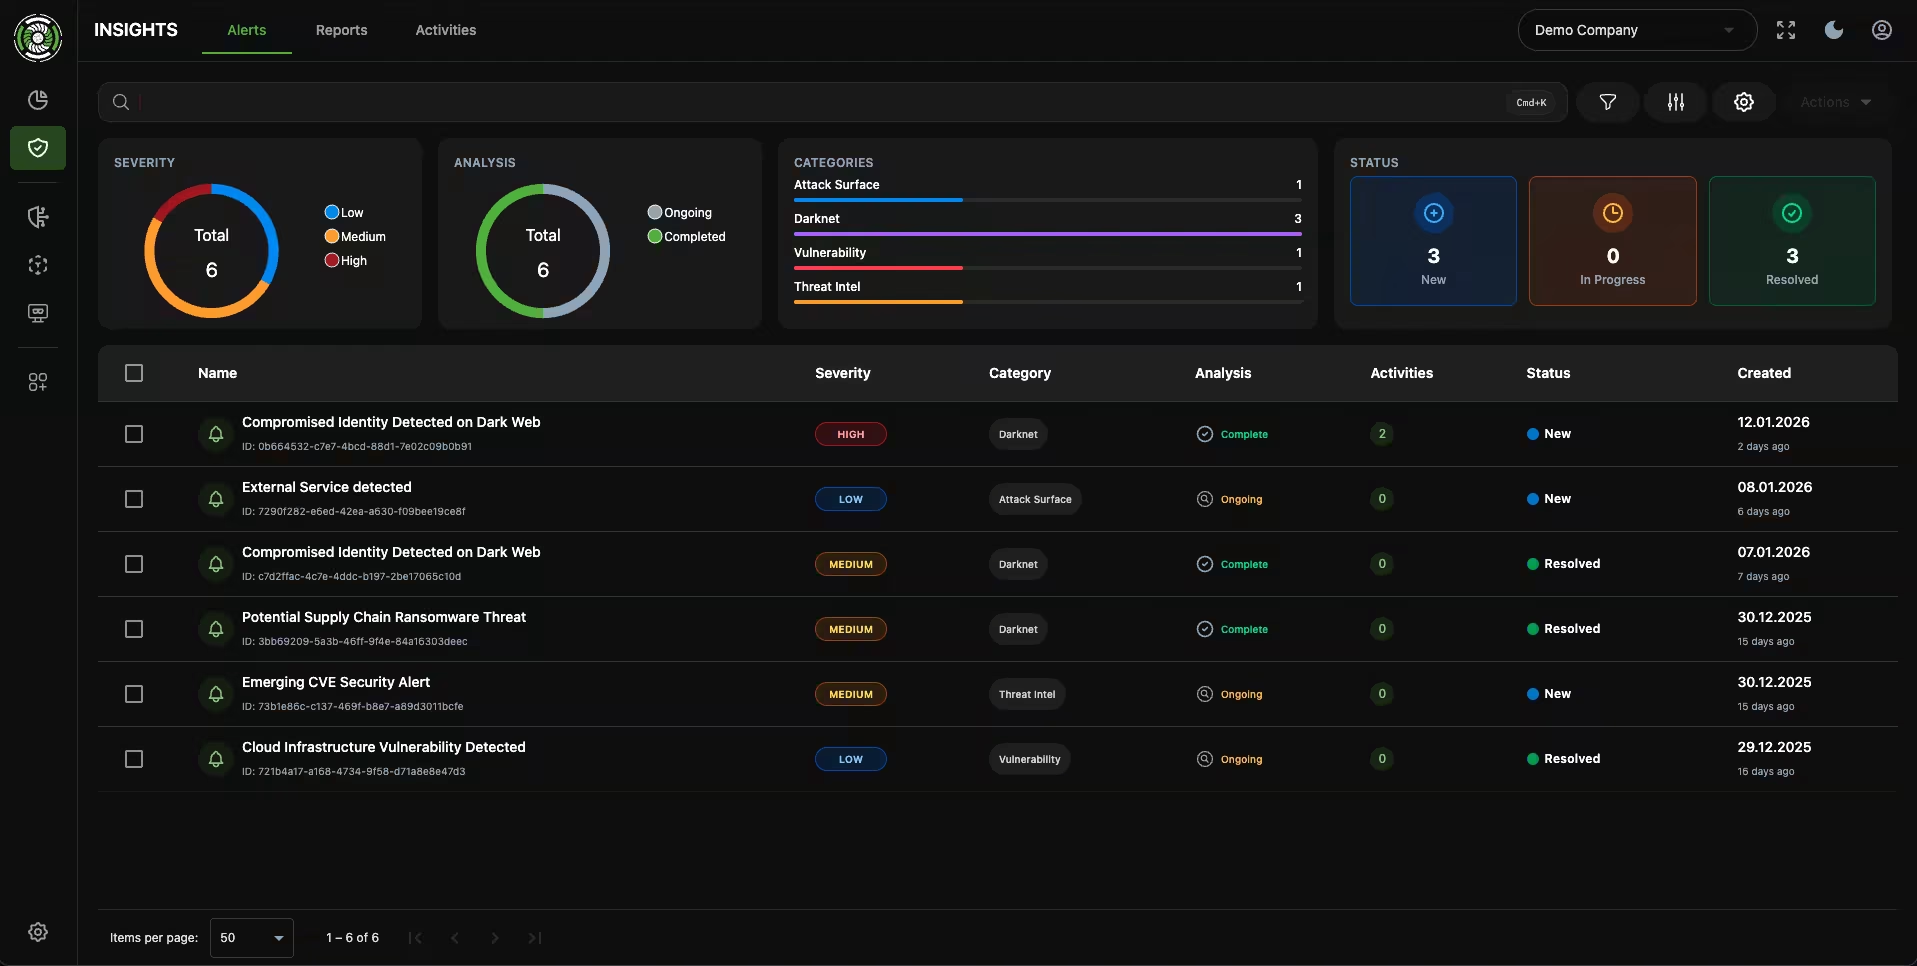
Unified Vulnerability Management: all sources, one process
Unified vulnerability management assesses findings from external and internal scans, cloud and pentests in one workflow: prioritised consistently, assigned and tracked until fixed.
A Europe-wide logistics provider assesses vulnerabilities from all networks, cloud accounts and subsidiaries centrally and consistently.
Evidence for ISO/IEC 27001as PDF
Vulnerability reportISO/IEC 27001 A.8.8monthly
Threat Center matchingISO/IEC 27001 A.5.7real time
Activity logISO/IEC 27001 A.8.16continuous
Visuals show sample data.
Reduced attack surface
A complete inventory across all subsidiaries.
Clear responsibilities
Every finding with status and owner.
Auditable under ISO 27001
Measures documented traceably.
Frequently asked questions
A vulnerability scanner produces findings. Unified vulnerability management is the process around them: consistent assessment across all sources, prioritisation by real risk, assignment, follow-up, retest and reporting. blacklens.io brings the scanners, that is 200,000+ daily updated tests for the external attack surface, Sentry for internal networks and 500+ CIS-aligned cloud checks, and adds this process in one shared data model.
blacklens.io prioritises by real risk rather than by the CVSS score alone. Every vulnerability carries its EPSS score and percentile, CISA KEV membership with due date and ransomware flag, public exploit and PoC availability, CVSS v3 and v4, CWE and the fixed version. If the EPSS score exceeds 0.80 and an exploit exists, the alert severity is raised automatically. The AI remediation plan groups open findings by shared root cause and ranks them by risk reduction.
blacklens.io brings its own scanners for external, internal (Sentry) and cloud; importing third-party scan results is not part of the platform. Results from blacklens.io, on the other hand, flow into your existing systems: via the REST API with 250+ endpoints, as CSV or PDF export, or through integrations with Jira, ServiceNow, Microsoft Sentinel, Elastic and webhooks.
On several levels: the Threat Center verifies exposure automatically with a targeted PoC scan before a finding counts as confirmed. Pentesters mark manually checked findings as verified. For the rest there are the statuses risk accepted and snoozed with a comment, so the decision is documented and does not have to be made again on every scan.
Every finding goes through the same lifecycle, whether it comes from external scans, Sentry, the cloud or a pentest: opened, in progress, snoozed, risk accepted and closed. Snoozed findings reopen automatically after 30 days. Fixed findings close by themselves on retest and are archived 30 days later. Comments, evidence images and the activity log document every decision.
The external attack surface is tracked continuously, cloud audits run every seven days by default and on demand, Sentry scans follow your schedule, new CVEs are matched in real time and dark web monitoring runs daily. The vulnerability tests are updated daily and alerts are collected every five minutes. Assets not seen for seven days disappear from the inventory automatically.
Sentry is a scanner appliance on the network, not software on every endpoint. It runs as a VM on VMware, Hyper-V or Proxmox or as a Docker container and reaches servers, clients, printers, cameras, network devices and OT components over the network; authenticated checks use stored credentials. That is why switches, hypervisors and storage systems are covered too, as well as Active Directory.