
Blacklens Query Language (BQL): efficient data search made easy
The Blacklens Query Language (BQL) filters every table view in blacklens.io by query, with autocomplete as you type and a query builder that needs no syntax.
- by blacklens.io Team
- Published
- 1 min read
The Blacklens Query Language (BQL) makes searching your attack surface much easier. With BQL you search and filter data in a targeted way and quickly gain a comprehensive overview. The reason: BQL is built into every table view in blacklens.io.
Writing queries with autocomplete
If you like writing your own queries, autocomplete helps. It simplifies query building and makes it more intuitive and less time-consuming: as you type, BQL suggests matching fields.

A query such as svc_name: https and http_status: 200, for example, narrows the list to HTTPS services that respond with status code 200.
Filters without syntax: the query builder
The query builder offers an even simpler route to a query. It suits anyone who prefers guided query building, and it lets you create complex data filters without memorising syntax or commands.
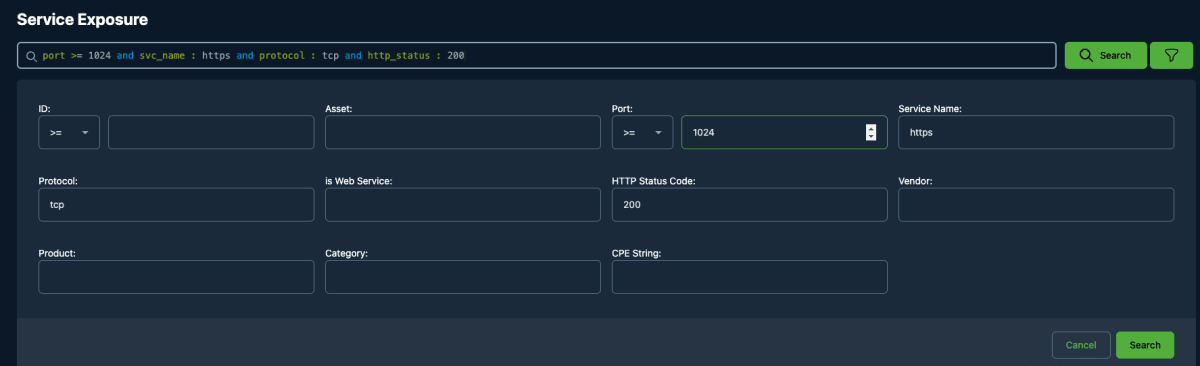
The values from the form fields end up as a finished query in the search bar, for example port >= 1024 and svc_name: https and protocol: tcp and http_status: 200.
What BQL brings to daily work
The Blacklens Query Language is more than a query tool. Whether through autocomplete, the query builder or by passing queries directly in the URL, BQL lets you navigate and analyse your attack surface data with one consistent query language – from exposed services to vulnerability management.
Frequently asked questions
- The Blacklens Query Language (BQL) is the query language of blacklens.io. It is built into every table view of the platform and filters data by field names, comparison operators and conditions joined with and, for example port >= 1024 and svc_name: https. That lets you search your attack surface in a targeted way and get an overview quickly, instead of working through long lists by hand.
More articles

HTTP2Shell: the Brotli flaw reaches far beyond Node.js
HTTP2Shell is not a new flaw but CVE-2026-111497 in any software with a Brotli decoder. Who is affected, and why the version number misleads.
- 5 min read

Node2Shell: why patching Node alone is not enough
Node2Shell exploits a flaw in the Brotli decoder that Node.js bundles. The fix ships in Node 22.23.4, 24.22.1 and 26.12.1 – and in Brotli itself.
- 5 min read

Fortinet hardening release: patching without an advisory
Fortinet shipped critical fixes for FortiOS, FortiManager and FortiAnalyzer on 22 October 2026. The advisories with CVE ids only follow on 10 November.
- 5 min read
See your attack surface within 24 hours.
We set up your workspace and walk you through the first findings.
- 14 days free, all features
- No credit card required
- We walk you through your first findings