
Dark Web Monitoring: cookies, AI analysis and leak classification
blacklens.io Dark Web Monitoring detects stolen session cookies, assesses them with AI and automatically assigns leaks to employees or customers.
- by blacklens.io Team
- Published
- Updated
- 2 min read
Data leaks, stolen session cookies and compromised credentials from the dark web are a constant risk for organisations and individuals alike. They can lead to financial losses and lasting reputational damage.
New capabilities in blacklens.io Dark Web Monitoring add three features: detection of stolen cookies, AI-based assessment of those cookies and simple classification of leaks.
The danger of stolen session cookies – and how blacklens.io detects them
Session cookies often act as the "key" to active user sessions. In the wrong hands, they become a serious security risk. Attackers can use stolen cookies to access accounts – no password required. The method is effective and hard to detect.
blacklens.io detects such cookies automatically. Alongside passwords and personally identifiable information (PII), the system now also detects compromised cookies, including session cookies. Automatic detection lets organisations act immediately and invalidate the affected sessions before greater damage is done.
AI-based assessment of stolen cookies
blacklens.io uses artificial intelligence to analyse stolen cookies. Organisations often find it hard to assess the risk of a particular leak quickly and accurately, especially when it involves stolen session cookies.
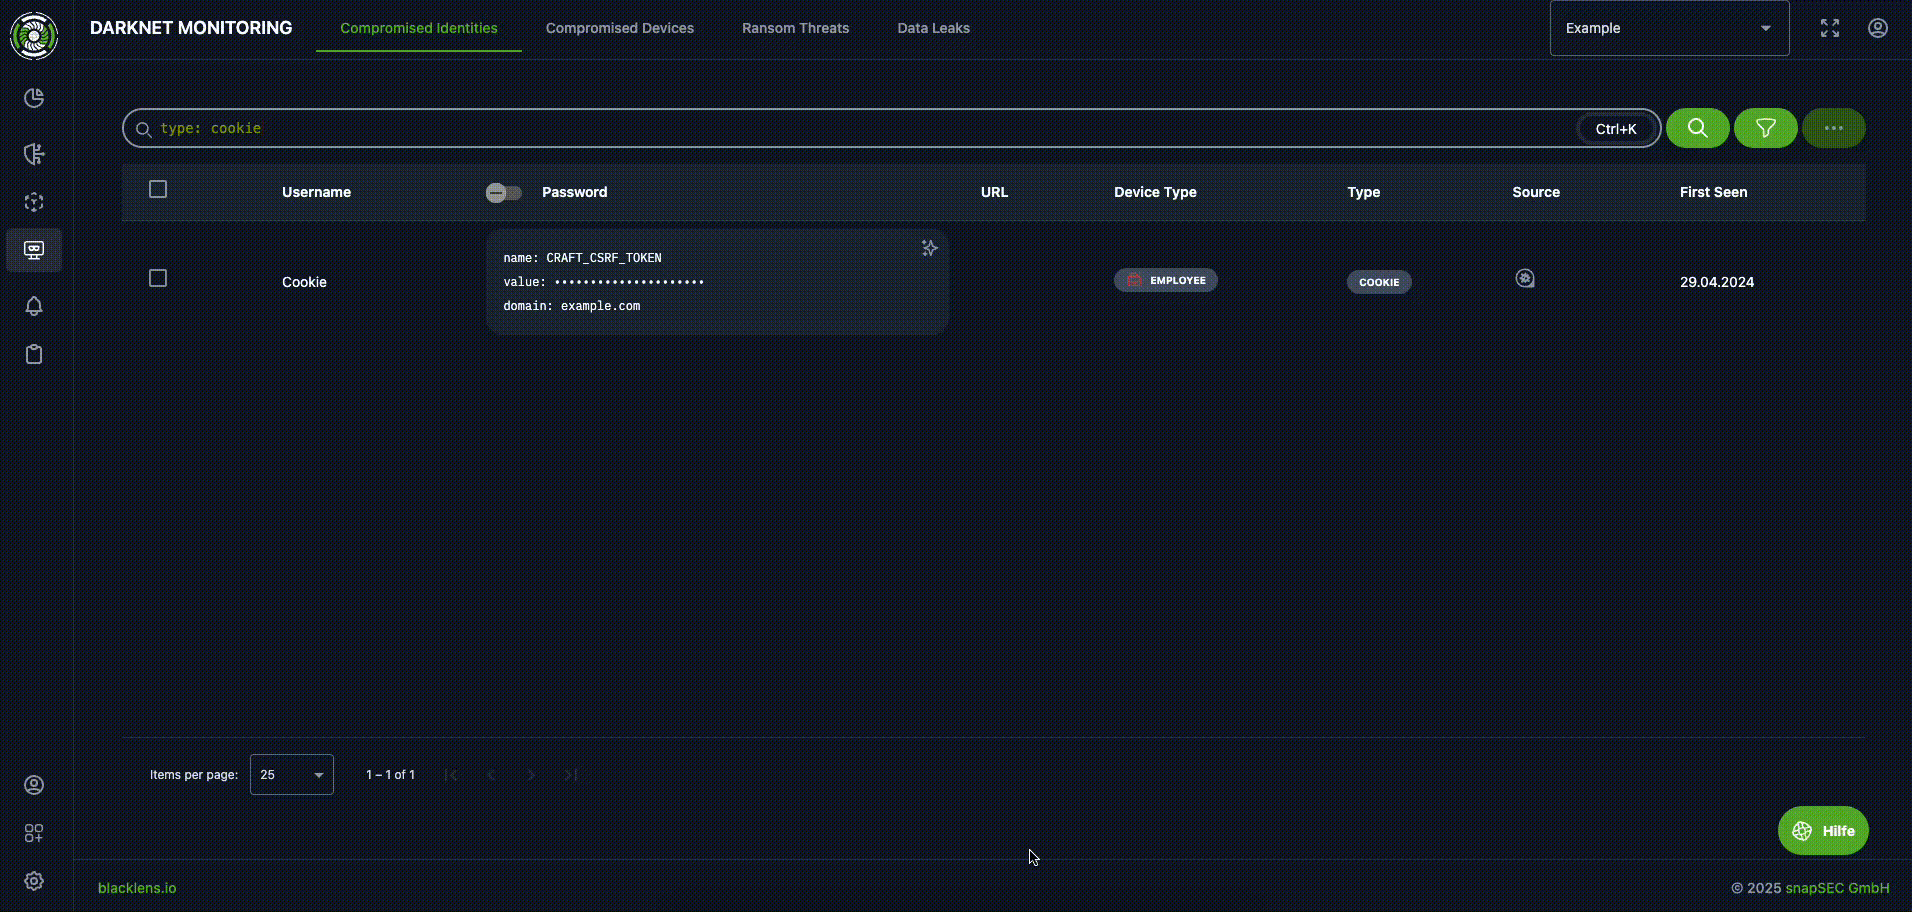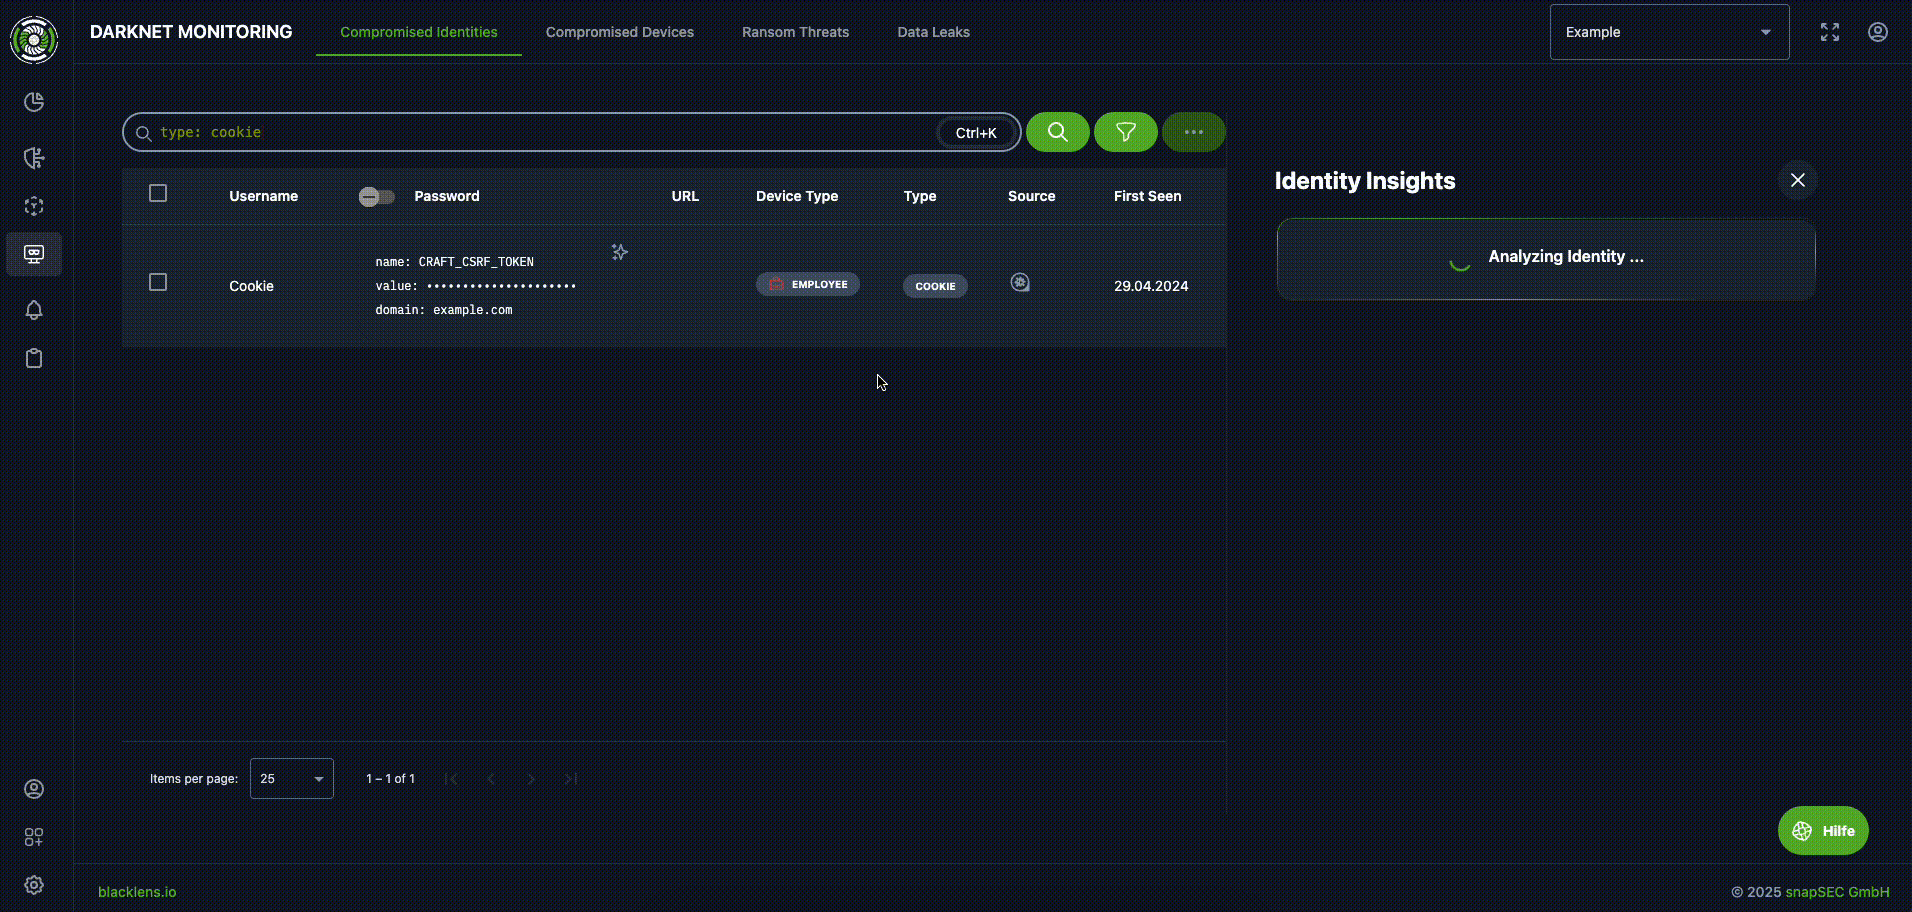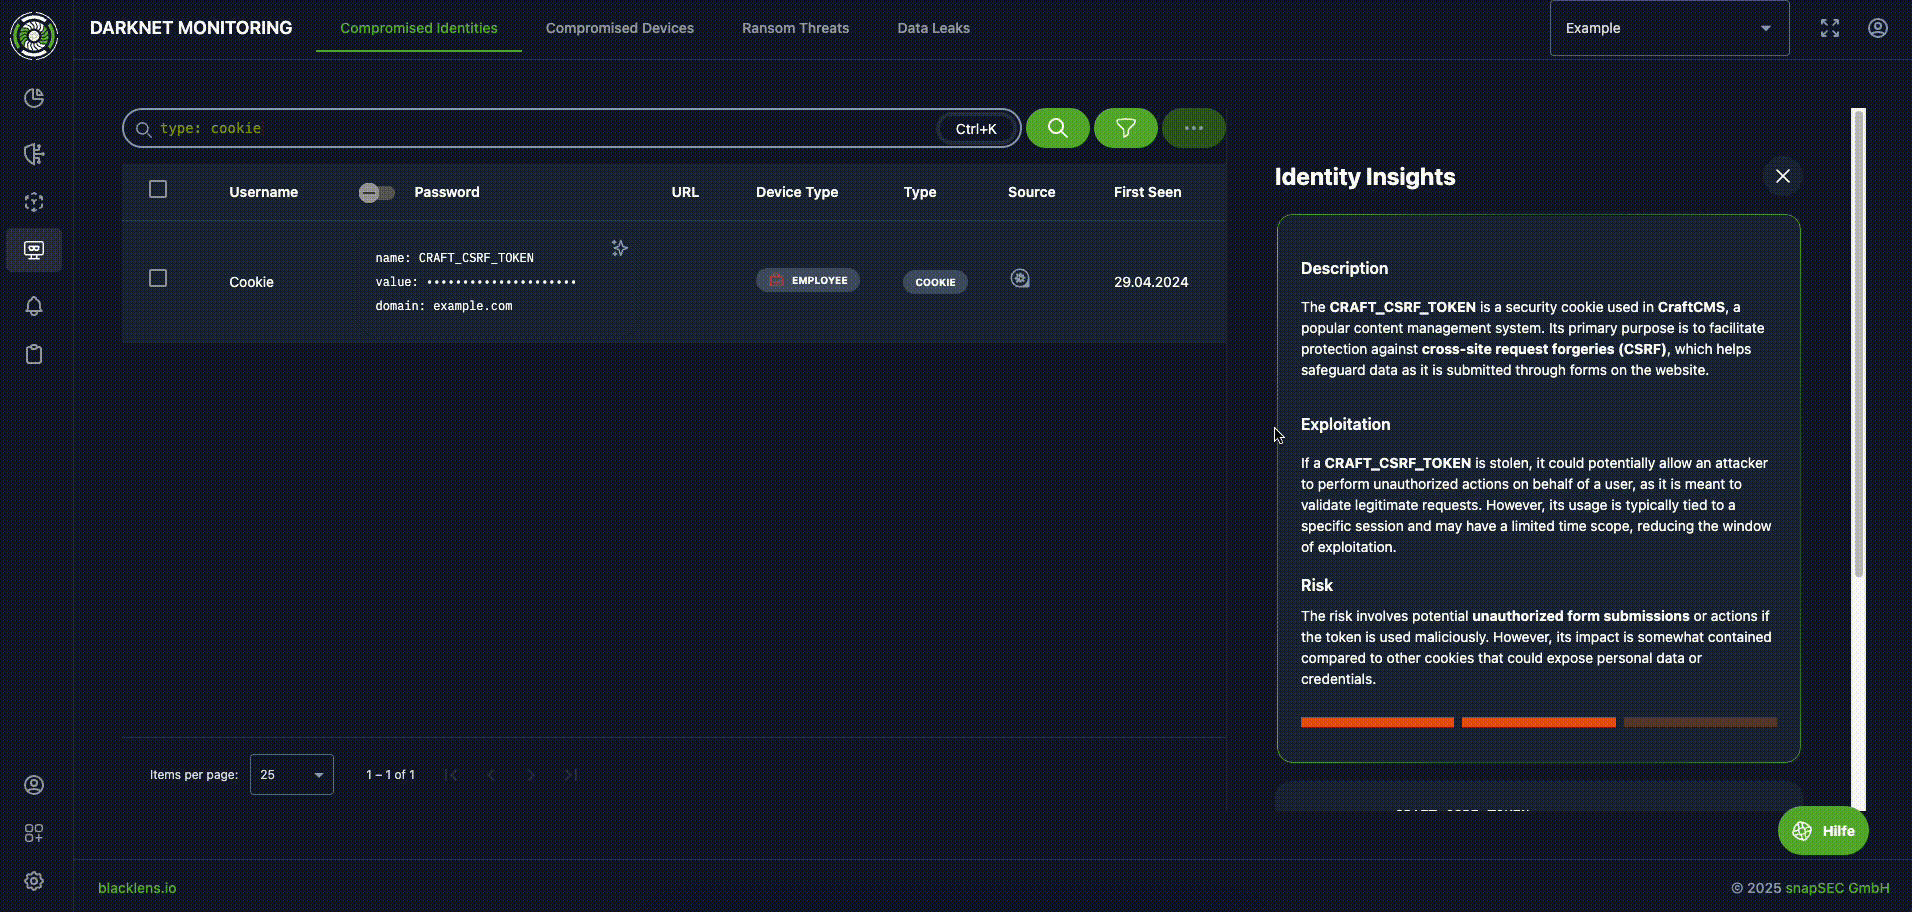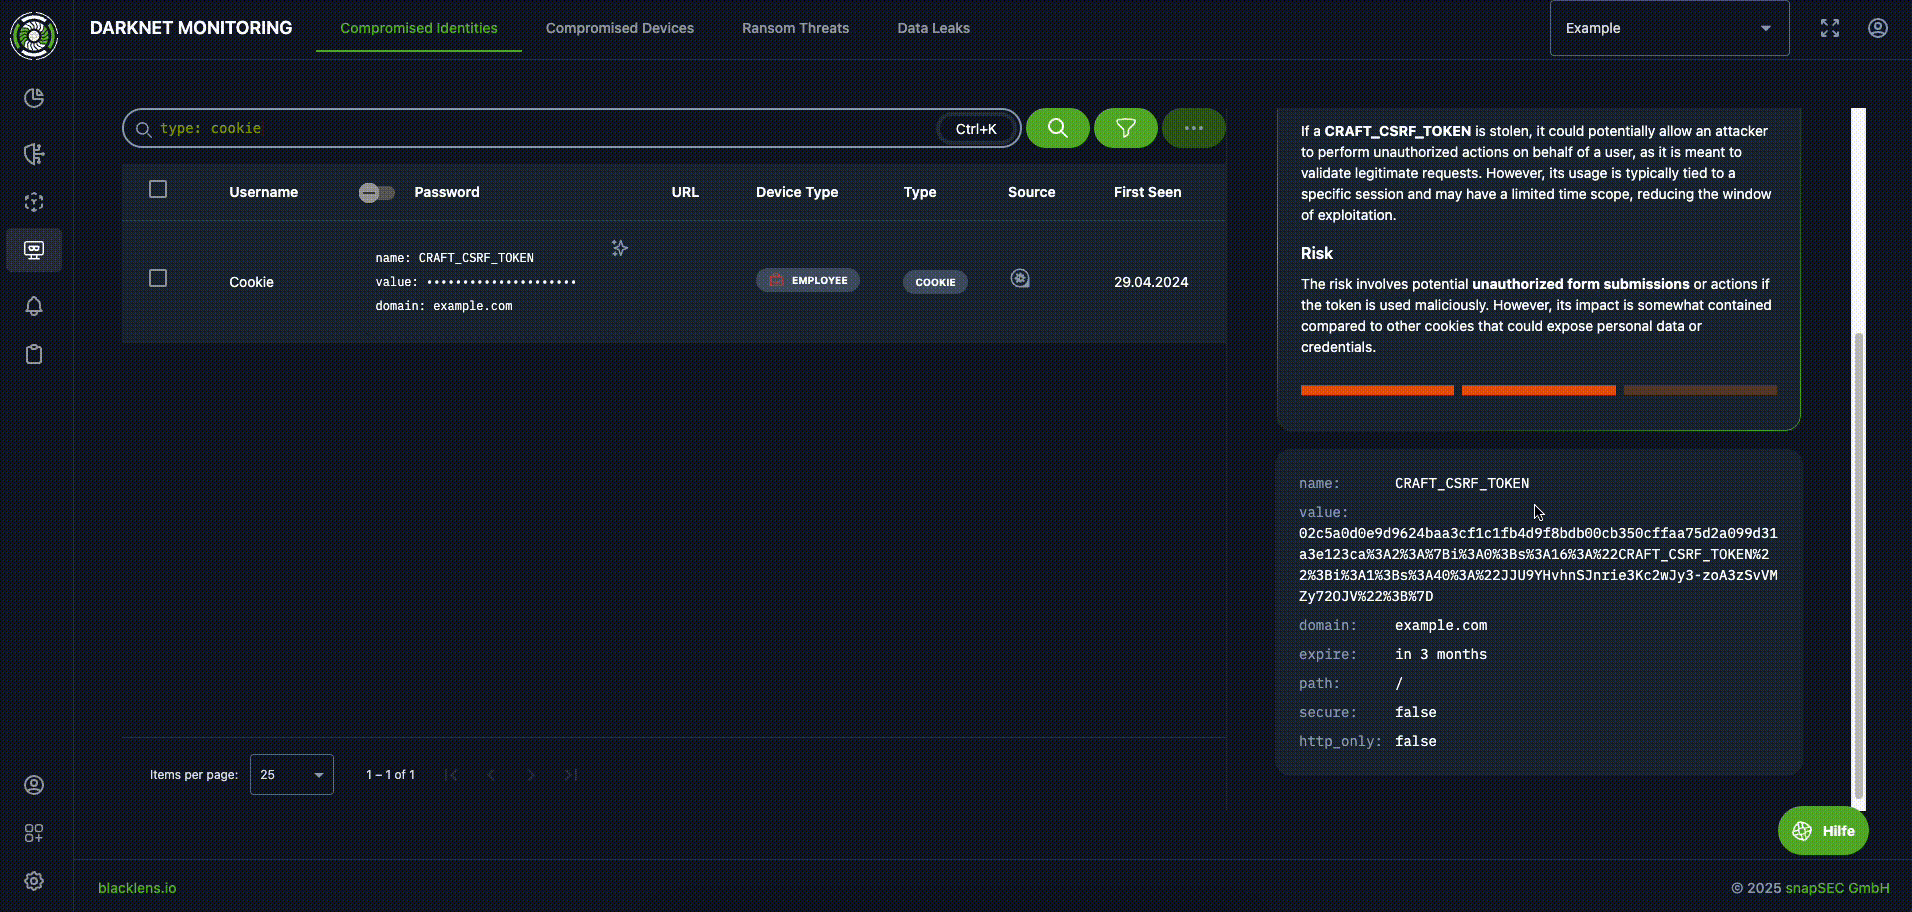
That is why blacklens.io delivers an AI-based assessment of compromised cookies. It relies only on the cookie's name, not its content, and checks the name against a public cookie database. The analyses explain what a cookie is for, how it can be exploited and how high the risk is. This helps security teams prioritise efficiently, take targeted measures and save time.
Classifying employee and customer leaks
Not all compromised identities are the same. Some concern employees, others customers – and some cannot be assigned easily.
Under Compromised Identities, blacklens.io gives a clear view of all compromised credentials and classifies them automatically into employees and customers. Leaks whose origin is unclear can be assigned through a selection menu – to an employee portal or a customer portal.
That makes it easier for organisations to take targeted measures and protect their employees' data as well as their customers'.
Conclusion
Automated cookie detection, AI-based risk analysis and simple classification together help organisations detect, analyse and contain threats from data leaks quickly.
Get started: you will find the features in blacklens.io under Darknet Monitoring → Compromised Identities. Read more about Dark Web Monitoring in blacklens.io on the platform page.
Frequently asked questions
- Stolen session cookies act like a key to a user session that is already logged in. Attackers use them to access accounts without knowing a password, and the method is hard to detect. When a compromised session cookie turns up, organisations should therefore invalidate the affected sessions immediately, before greater damage is done.
More articles

HTTP2Shell: the Brotli flaw reaches far beyond Node.js
HTTP2Shell is not a new flaw but CVE-2026-111497 in any software with a Brotli decoder. Who is affected, and why the version number misleads.
- 5 min read

Node2Shell: why patching Node alone is not enough
Node2Shell exploits a flaw in the Brotli decoder that Node.js bundles. The fix ships in Node 22.23.4, 24.22.1 and 26.12.1 – and in Brotli itself.
- 5 min read

Fortinet hardening release: patching without an advisory
Fortinet shipped critical fixes for FortiOS, FortiManager and FortiAnalyzer on 22 October 2026. The advisories with CVE ids only follow on 10 November.
- 5 min read
See your attack surface within 24 hours.
We set up your workspace and walk you through the first findings.
- 14 days free, all features
- No credit card required
- We walk you through your first findings